
- Business Email Compromise Is a Targeted Email Scam
- How BEC Attacks Unfold Inside Real Workflows
- Common Forms of BEC
- Why BEC Is Harder to Catch Than Ordinary Phishing
- Who Attackers Target and What the Business Risks
- How to Prevent Business Email Compromise
- What to Do After a Suspected BEC Incident
- FAQ
- How 1Byte Helps Reduce BEC Risk
- Conclusion
Business Email Compromise is a targeted email scam where an attacker pretends to be a trusted person or organization to trick someone into sending money, changing payment details, or sharing sensitive information. It usually targets real business workflows, such as invoice approval, wire transfers, payroll updates, vendor payments, or executive requests. The danger is that the message often looks boring and normal, which is exactly why it works. We see BEC as one of the clearest reminders that security is not just a firewall problem, it is a people, process, and identity problem.
Unlike noisy phishing blasts, Business Email Compromise often arrives as a short, believable request. It may contain no malware, no strange attachment, and no obvious spelling errors. The attacker wins by understanding how the company already communicates. If the victim acts before verifying the request, a routine email can turn into a costly fraud case.
Business Email Compromise Is a Targeted Email Scam
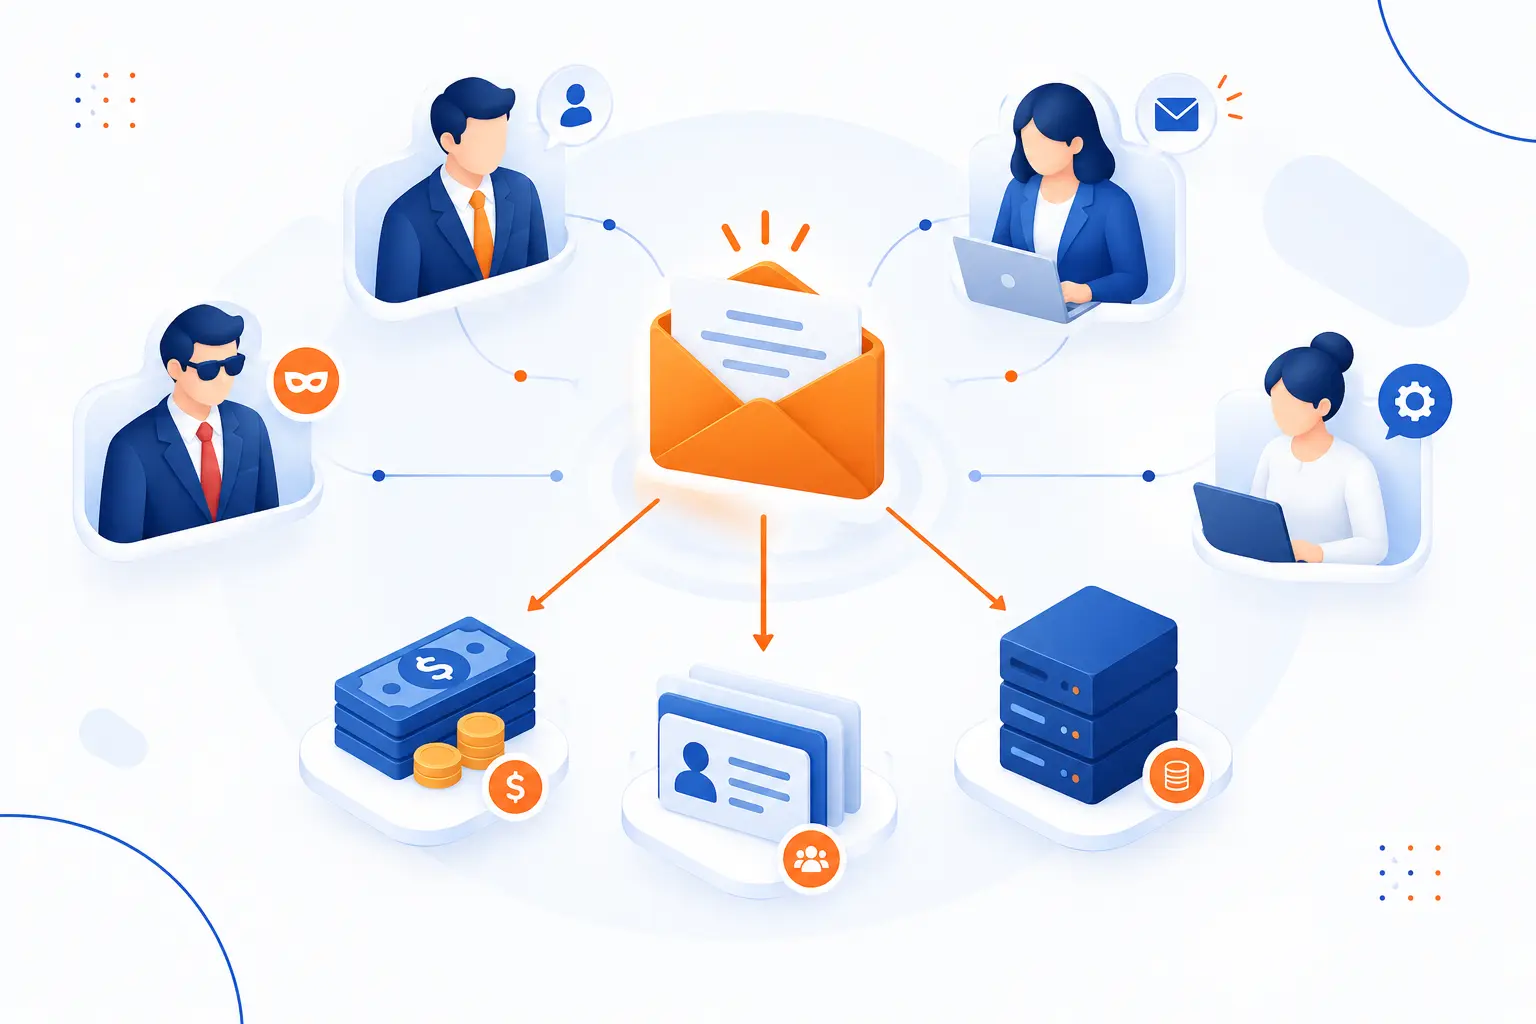
Business Email Compromise is a scam that uses trusted business relationships to manipulate payment, payroll, or data-sharing decisions. The attacker may impersonate an executive, supplier, lawyer, bank, customer, or internal employee. The goal is usually financial theft, although stolen tax records, employee data, and login credentials can also be valuable. The FBI’s latest annual reporting shows why this topic deserves board-level attention: reported losses reached $3,046,598,558 in reported losses.
FURTHER READING: |
| 1. Cloud Mail Security Guide for Safer Business Email |
| 2. What Is API Security and How Do You Protect It |
| 3. What Are Web Application Firewalls and How They Work |
It Uses Impersonation to Steal Money or Sensitive Data
BEC works because the attacker borrows someone else’s authority, trust, or business role. A finance employee may receive a message that appears to come from the CEO. An HR manager may get a payroll update from what looks like an employee’s personal email. A buyer may receive “new bank details” from a vendor contact they already know.
The impersonation can be simple or highly polished. Some attackers use lookalike domains, such as replacing one letter in a company name. Others compromise a real mailbox and send from the genuine account. That second case is especially dangerous because the message may pass basic sender checks and appear inside an existing thread.
It Often Looks Legitimate Because It Mimics Normal Business Communication
A BEC message often looks legitimate because it copies the rhythm of ordinary work. The attacker may use the same invoice numbers, project names, email signatures, greetings, and approval language that employees expect. That is why we warn teams not to rely on “does it look professional?” as a security test.
Real-world losses show how ordinary this can look from the inside. Ubiquiti disclosed that employee impersonation and fraudulent requests targeting its finance department led to transfers totaling $46.7 million. The lesson is blunt: polished business language is not proof of authenticity.
How BEC Attacks Unfold Inside Real Workflows
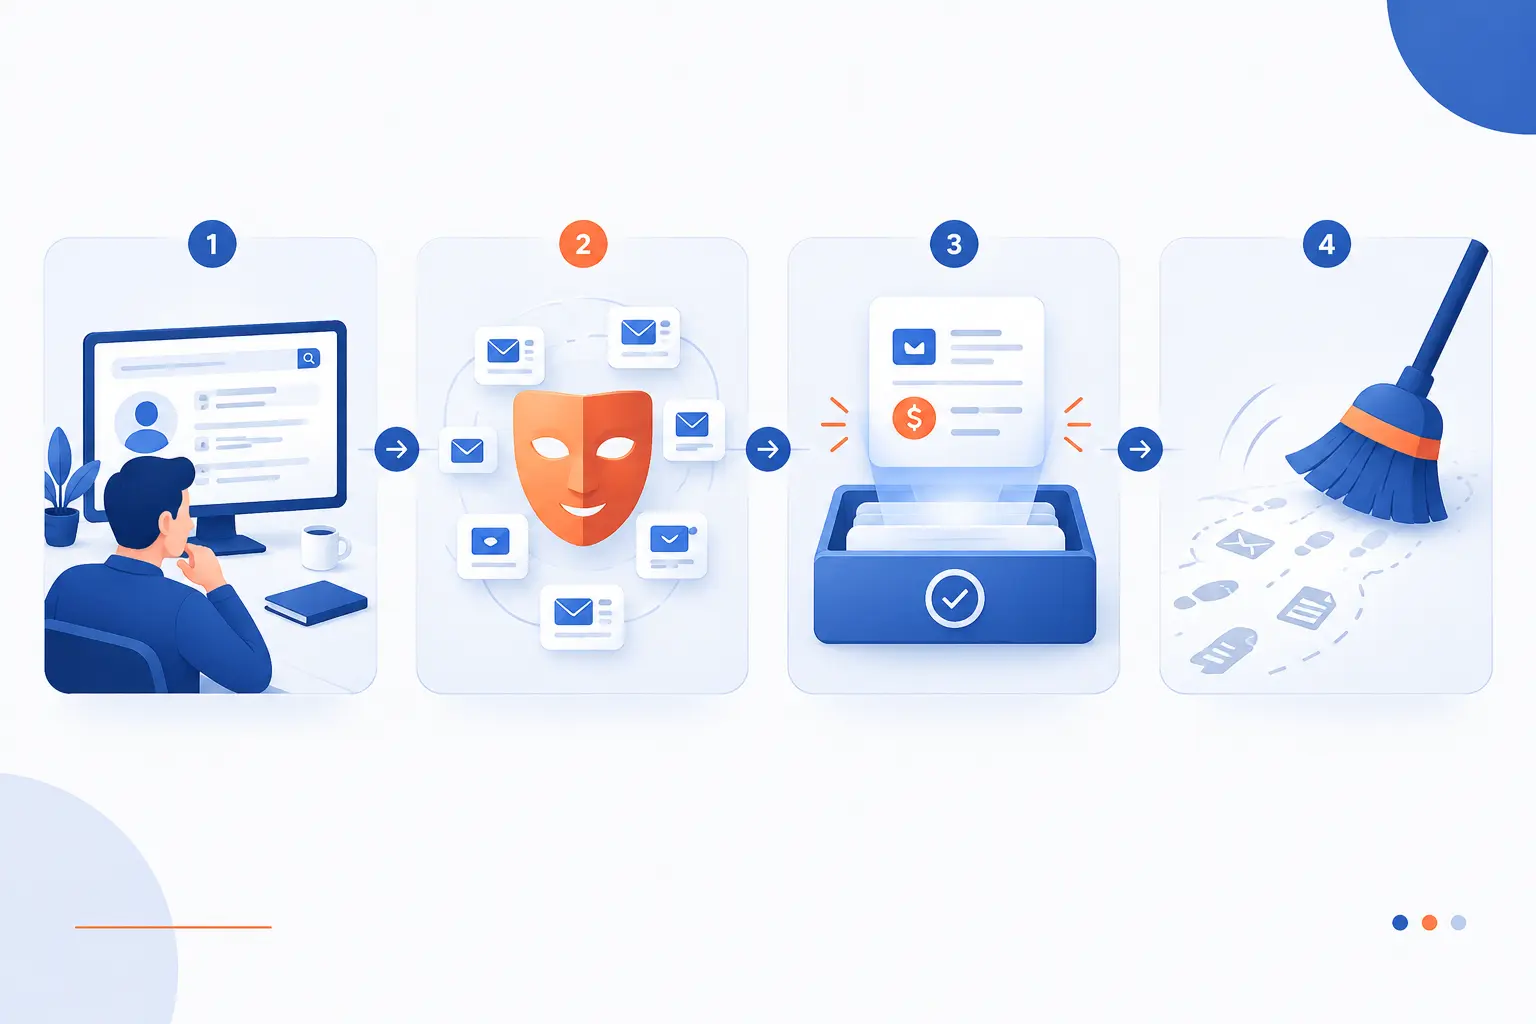
BEC attacks usually unfold as a patient sequence: research the company, gain a believable identity, blend into a workflow, request a payment or data change, then hide the evidence. The attacker does not need to “hack everything” if one trusted message can change a bank account. This is why prevention must combine account security, payment controls, and human verification. We like to think of BEC as process fraud delivered by email.
Researching the Organization and Its Decision Makers
Attackers begin by learning who can approve, request, or influence money movement. They scan company websites, LinkedIn profiles, press releases, procurement pages, court filings, job posts, and social media. A public post about a new CFO, a conference trip, or a vendor migration can become useful bait.
This research helps attackers choose the right target. Finance staff, payroll teams, executive assistants, and vendor managers are obvious choices. But the attacker may also target a lower-level employee who can forward a request to someone with authority. In our view, this is where BEC becomes more like reconnaissance than spam.
Using Phishing, Domain Spoofing, or Stolen Credentials to Gain Access
Attackers use phishing, spoofing, lookalike domains, or stolen credentials to make the request look credible. A phishing page may capture a Microsoft 365 or Google Workspace password. A lookalike domain may differ from the real one by a single character. A stolen password may give the attacker the most convincing asset of all: a real inbox.
Technical email controls help, but they are not magic. SPF tells receiving systems which servers may send for a domain, DKIM signs messages, and DMARC connects authentication results to the visible sender domain through alignment rules described in the standards record. These controls reduce spoofing risk, yet they do not stop a fraudster who is already inside a valid account.
Blending Into Existing Conversations and Building Trust
The most dangerous BEC attacks often blend into conversations already in progress. If an attacker controls a vendor mailbox, they can wait until an invoice is due, then reply in the same thread with updated bank details. The victim sees familiar names, familiar context, and a normal business reason to act.
Trust builds through timing. The attacker may ask small questions first, such as whether an invoice has been received. Later, they introduce a payment change. That slow approach lowers suspicion because it feels like a continuation of regular work.
Redirecting Payments, Payroll, or Confidential Records
The payoff usually comes when the attacker redirects money or sensitive records. They may ask for a wire transfer, ACH change, payroll deposit update, gift card purchase, tax form, customer list, or login file. Payment redirection is common because it converts trust into cash quickly.
Payroll diversion deserves special attention. The attacker may impersonate an employee and ask HR to update direct deposit details before the next pay cycle. No invoice is involved. No executive is involved. It still causes direct financial harm and a difficult employee conversation.
Hiding Activity With Inbox Rules, Monitoring, or Reply-To Tricks
Attackers hide activity by creating forwarding rules, deleting messages, moving replies, or changing the reply-to address. In a compromised mailbox, they may route messages containing words like “invoice,” “payment,” or “suspicious” into a hidden folder or external account. This keeps the real user from seeing warnings.
Microsoft’s guidance notes that malicious inbox rules can forward mail, delete traces, or move messages into less noticeable folders, which is why administrators should monitor for suspicious rule creation through mailbox investigation steps. We have a simple opinion here: after a suspected BEC event, checking only the password is not enough.
Common Forms of BEC
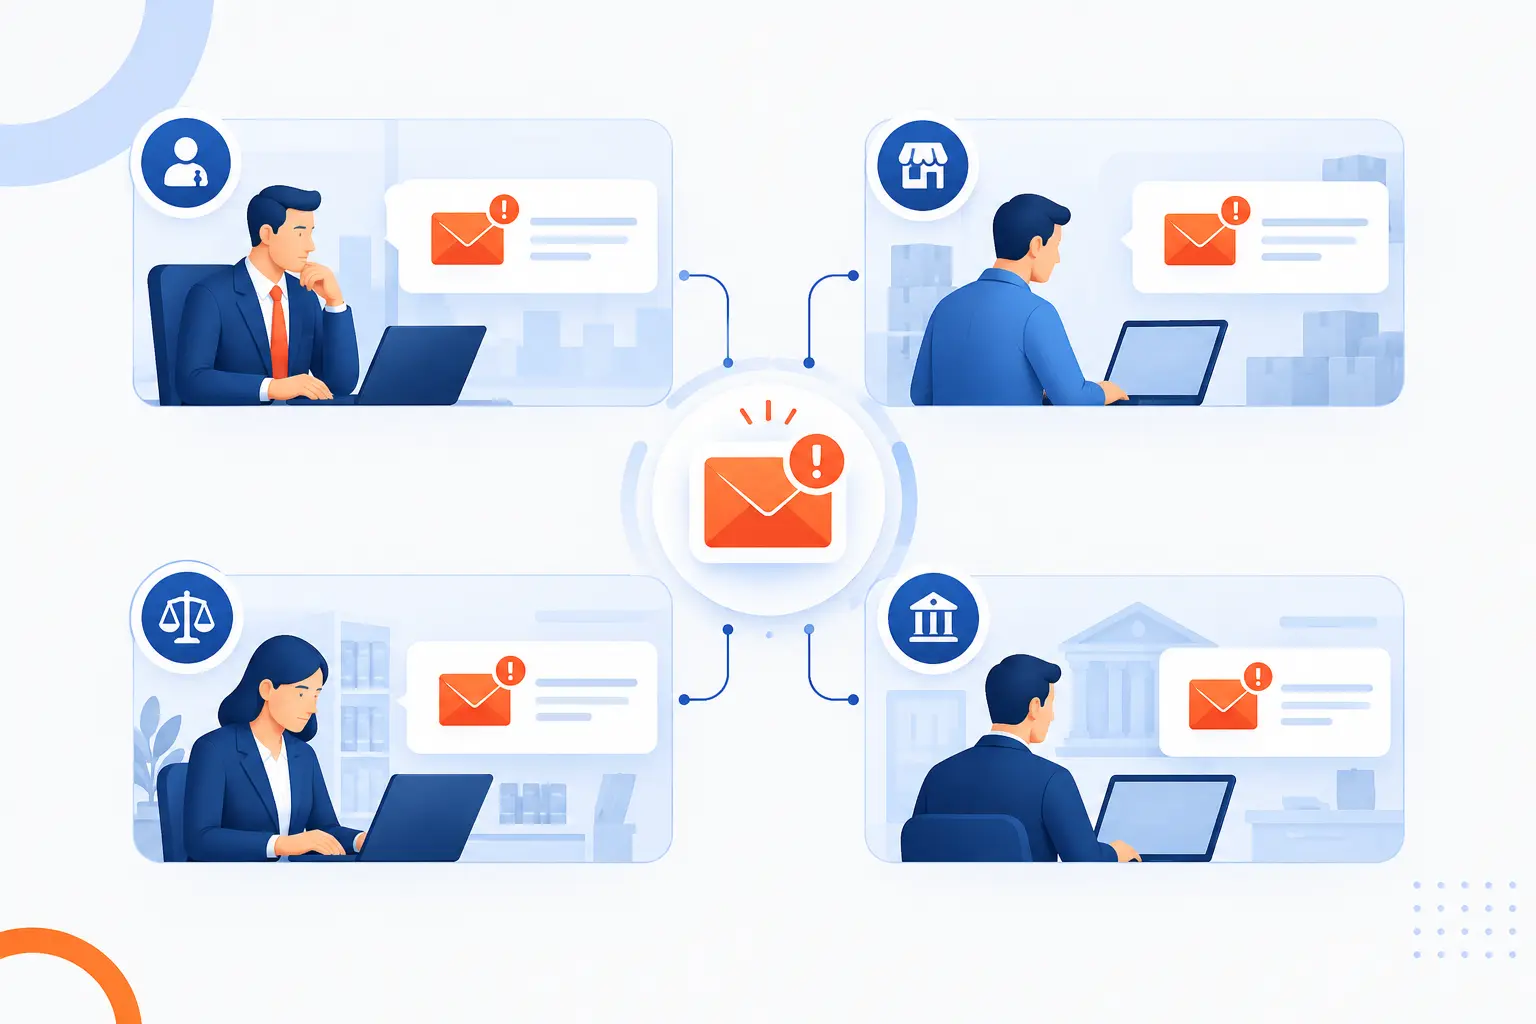
Common BEC forms differ by who is impersonated and what action the victim is pushed to take. Some attacks pretend to come from executives, while others abuse vendors, lawyers, banks, or real employee accounts. The shared pattern is trust plus urgency. This table gives a quick map before we walk through each form.
| Form | Typical Target | Main Risk |
|---|---|---|
| Executive impersonation | Finance staff | Unauthorized wire transfer |
| Vendor impersonation | Accounts payable | Payment to wrong account |
| Account abuse | Internal and external contacts | Fraud from a real mailbox |
| Payroll diversion | HR and payroll | Salary sent to attacker |
Executive Impersonation and Wire Transfer Fraud
Executive impersonation uses the perceived authority of a senior leader to pressure an employee into moving money. The email may say the CEO is in a meeting, traveling, or working on a confidential deal. The target is often told to act quickly and keep the request private.
This scam succeeds when authority overrides process. A junior employee may feel uncomfortable challenging a senior leader. That discomfort is exactly what the attacker wants. We prefer cultures where “I need to verify this” is seen as professional, not disobedient.
Vendor and Trusted Contact Impersonation
Vendor impersonation tricks a company into paying a real bill to a fake account. The attacker may claim that the vendor changed banks, updated its remittance address, or needs payment routed through a new subsidiary. Because the invoice may be real, the fraud hides inside a legitimate payable.
This form is common because vendor relationships rely on routine. If your team pays the same supplier every month, a small change may not feel risky. That is why bank detail changes should always trigger independent verification using a known contact method.
Compromised Email Account Abuse
Compromised account abuse happens when attackers use a real mailbox to send fraudulent requests. This is more convincing than spoofing because the sender address is genuine. It may also expose old invoices, signatures, deal history, and private conversations.
Once inside, the attacker can study writing style and timing. They can also contact customers and vendors from the compromised account. The harm spreads outward because recipients trust the relationship, not just the technology behind the message.
False Invoices and Billing Detail Changes
False invoices and billing changes exploit the normal pressure to pay bills on time. A fake invoice may look like office supplies, software, advertising, hosting, legal work, or a renewed service. A bank-detail update may appear as a short note attached to a familiar invoice.
The FTC warns that scammers create phony invoices that look tied to products or services a business uses, hoping the person who pays bills will assume they are real through small business guidance. Our practical rule is simple: an invoice can be familiar and still be fraudulent.
Attorney or Bank Impersonation
Attorney or bank impersonation uses professional authority to make the victim act fast. The attacker may refer to a closing, settlement, acquisition, audit, loan, or urgent compliance matter. Legal and financial language gives the request weight.
These scams often appear near major transactions. Real estate closings are a classic example because large wire transfers are expected. The safest response is to call a known number already on file, not the number in the email.
Payroll Diversion and HR Data Theft
Payroll diversion changes an employee’s direct deposit details so wages go to the attacker. HR data theft may request W-2 forms, passport scans, benefits data, or employee lists. These attacks target people who are trained to help employees quickly.
The request may arrive from a personal email address with a story about losing access to the work account. Sometimes that story is true, which makes blanket rejection hard. The better policy is structured verification before any payroll or personal data change.
Why BEC Is Harder to Catch Than Ordinary Phishing

BEC is harder to catch than ordinary phishing because it often lacks the signals security tools expect. There may be no malicious attachment, no suspicious link, and no bulk sending pattern. The message may be text-only and sent to one person. In our experience, BEC sits in the awkward space between cybersecurity, accounting controls, and workplace psychology.
Text-Only Messages Create Fewer Technical Red Flags
Text-only BEC messages create fewer technical red flags because there may be nothing for antivirus or link scanners to inspect. A message that says “Please process this payment today” is not malware. It is a business instruction, unless the context is wrong.
That makes detection harder. Security tools can analyze sender reputation, login patterns, and authentication results, but they cannot always know whether a payment request is valid. This is why payment workflow design matters as much as email filtering.
Social Engineering Exploits Authority, Urgency, and Familiarity
BEC exploits authority, urgency, and familiarity because people often respond to pressure before they verify details. The attacker may invoke a boss, a deadline, a late fee, a confidential deal, or a customer relationship. These triggers are powerful because they resemble real business pressures.
Training should not shame employees for falling for clever manipulation. A better approach teaches pause points. If a request involves money, credentials, payroll, secrecy, or changed sender details, employees should slow down and verify.
Legitimate Accounts and Lookalike Domains Can Pass Basic Checks
Legitimate accounts and lookalike domains can pass basic checks because they may not be technically forged. If an attacker signs in with valid credentials, the email really does come from that account. If a lookalike domain has proper email authentication, it may also pass basic domain checks.
This is where many companies learn a painful lesson. Email authentication can prove something about the sending domain, but it cannot prove the business intent behind the request. Controls must check both identity and transaction risk.
Who Attackers Target and What the Business Risks
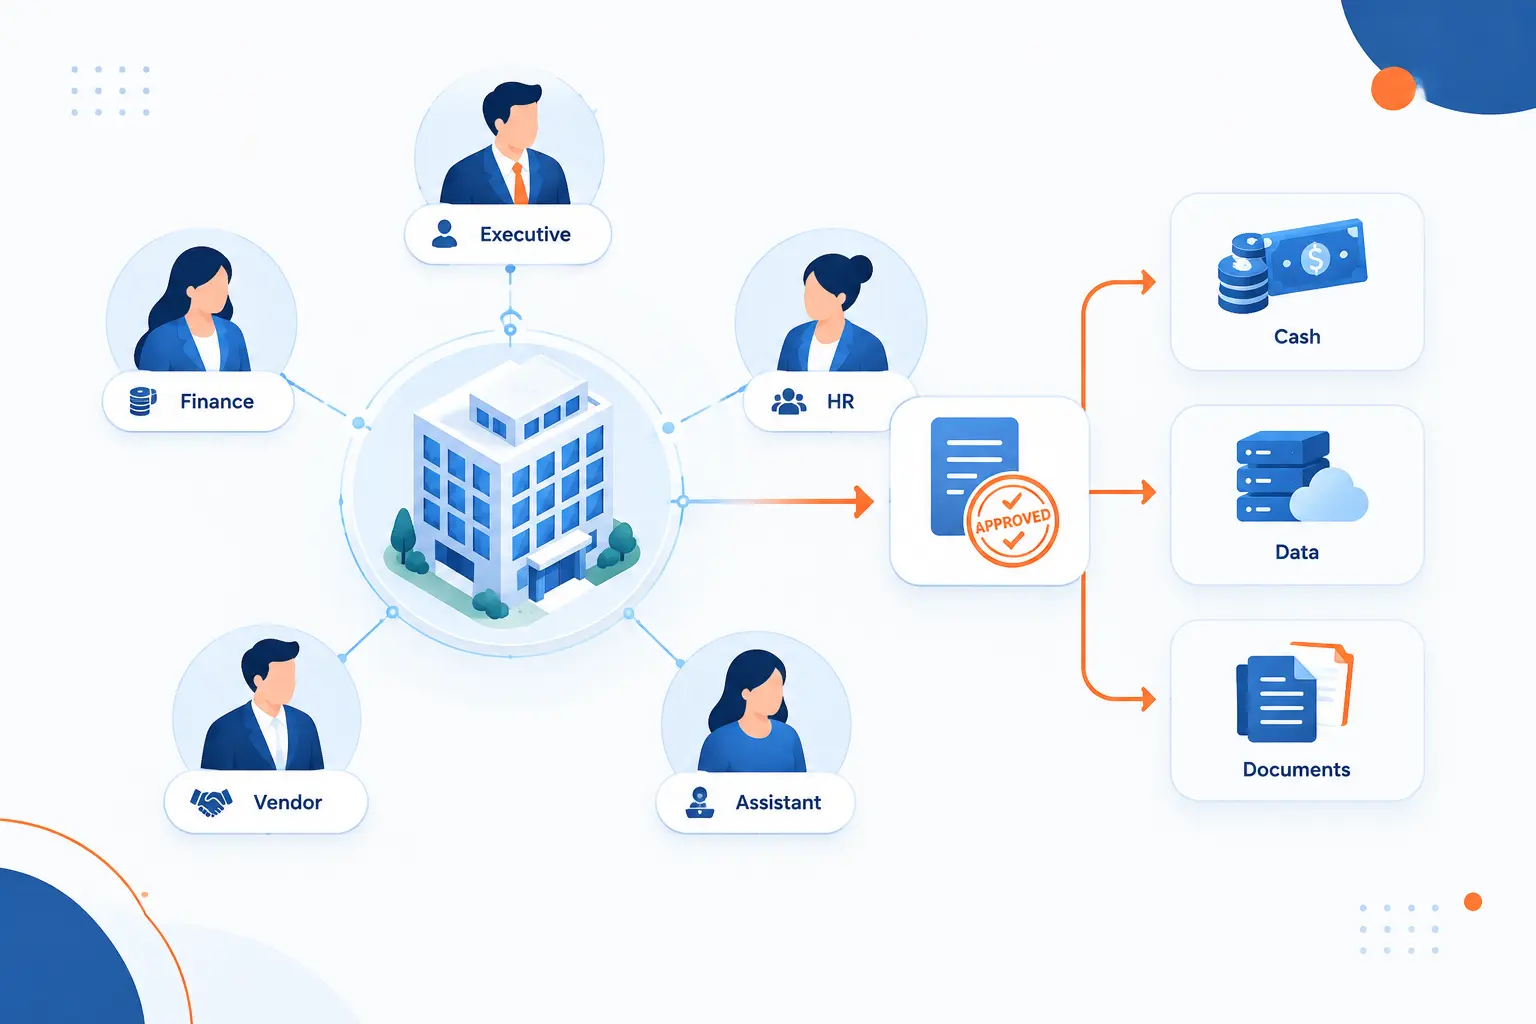
Attackers target people who can approve payments, change records, or influence trusted decisions. Finance, HR, executives, vendors, and assistants are common targets because their daily work involves sensitive action. The risks include lost funds, exposed data, legal costs, operational disruption, and reputational damage. For small businesses, one successful BEC incident can create a cash-flow problem almost overnight.
Finance and Accounts Payable Teams
Finance and accounts payable teams are prime targets because they handle invoices, wires, ACH updates, and vendor records. Attackers know these teams are measured on accuracy and timeliness. A request that looks like a routine payment can slip into the queue.
The highest-risk moments include vendor onboarding, bank-detail updates, month-end close, and urgent executive payments. We recommend treating those moments like controlled checkpoints. A little friction here is cheaper than a fraudulent transfer.
Human Resources and Payroll Staff
HR and payroll staff are targeted because they control salary routing and employee records. An attacker may ask to update direct deposit, resend tax forms, or confirm personal data. These requests often sound human and harmless.
The challenge is that HR teams are service-oriented. They want to help. A good security process should support that instinct while adding verification. For example, payroll changes can require confirmation through an employee portal or a known phone number.
Executives, Vendors, and Other High-Trust Contacts
Executives, vendors, and high-trust contacts are targeted because their names make requests persuasive. Attackers may compromise an executive assistant, a vendor’s accounts receivable inbox, or a contractor who regularly exchanges invoices. Trust flows through the relationship.
This risk extends beyond your own company. A supplier with weak mailbox security can become the path into your payment process. That is why vendor management should include contact verification and change-control procedures, not just contract terms.
Losses That Extend to Cash Flow, Data, and Reputation
BEC losses extend beyond the stolen payment because the incident can interrupt operations, expose data, and damage trust. A company may spend weeks working with banks, insurers, lawyers, customers, vendors, and law enforcement. Employees may also lose confidence in internal systems.
Cash-flow harm can be especially sharp for smaller firms. If rent, payroll, or supplier funds are diverted, the business still owes the legitimate party. The attacker may be gone, but the obligation remains.
How to Prevent Business Email Compromise
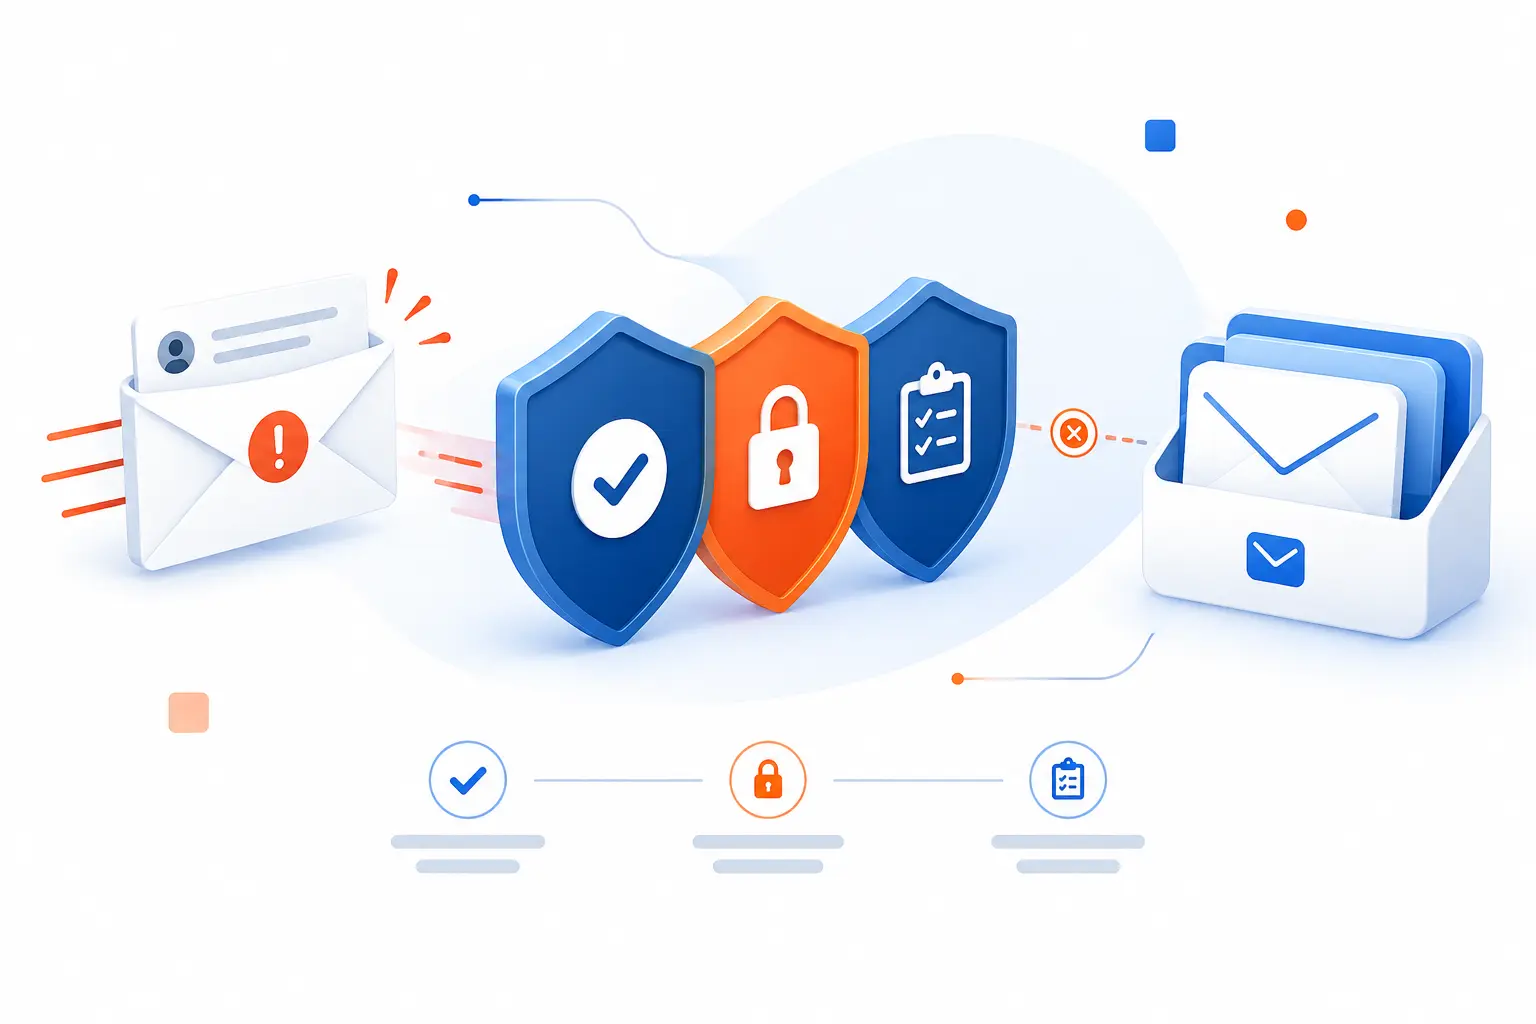
The best way to prevent Business Email Compromise is to combine human verification, email authentication, account protection, approval controls, and continuous monitoring. No single tool solves BEC because the attack crosses technical and business boundaries. Strong prevention makes suspicious requests harder to send, harder to believe, and harder to approve. We favor controls that are boring, repeatable, and written into daily workflow.
Verify Payment and Account Changes Through Trusted Offline Channels
Verify every payment or account change through a trusted channel that is already on file. Do not use the phone number, email address, or bank contact included in the new message. Use vendor records, contract files, a procurement system, or a known direct number.
This habit blocks many BEC attempts because it breaks the attacker’s control of the conversation. The FTC gives similar advice for imposter scams: contact the real company or person through information you know is legitimate, not the details supplied in the suspicious message through consumer protection advice.
Use MFA, SPF, DKIM, and DMARC to Tighten Account Security
Use MFA, SPF, DKIM, and DMARC because they reduce account takeover and domain spoofing risk. MFA makes stolen passwords less useful. SPF, DKIM, and DMARC help receiving systems evaluate whether mail using your domain is authorized and aligned.
For privileged and finance-related accounts, phishing-resistant authentication is even better where feasible. NIST describes phishing resistance as preventing disclosure of authentication secrets or valid outputs to an impostor verifier without depending on user vigilance in federal authentication guidance. That matters because BEC often starts with a stolen password.
Train Employees to Question Urgency, Secrecy, and Sender Changes
Train employees to question urgency, secrecy, and sender changes because those are common manipulation signals. A message that says “do this now,” “keep this confidential,” or “I changed banks” should not move straight to action. It should move to verification.
Good training uses examples from actual workflows. Show finance staff fake bank-change notices. Show HR staff payroll-diversion emails. Teach executives to welcome verification instead of punishing it. Culture beats posters on a wall.
Require Dual Approval for Wires, ACH Changes, and High-Risk Requests
Require dual approval for wires, ACH changes, payroll updates, and sensitive data requests. One person should not be able to receive, approve, and execute a high-risk change alone. Separation of duties gives the organization a second chance to catch fraud.
Dual approval should be meaningful. The second reviewer must check the request source, payment details, vendor record, and verification evidence. A rubber stamp is theater. A real control asks, “How do we know this change is authentic?”
Monitor for Forwarding Rules, Unusual Logins, and Suspicious Domains
Monitor for forwarding rules, unusual logins, and suspicious domains because BEC attackers often leave traces before the money moves. New inbox rules, impossible travel logins, fresh MFA registrations, unfamiliar OAuth apps, and recent external forwarding can all matter. Domain registrations that imitate your brand can also signal preparation.
Microsoft recommends checking compromised mailboxes for suspicious forwarding settings, hidden inbox rules, and sign-in activity in its account recovery procedure. We would add one practical point: make monitoring someone’s job before an incident, not a panicked task after funds vanish.
What to Do After a Suspected BEC Incident
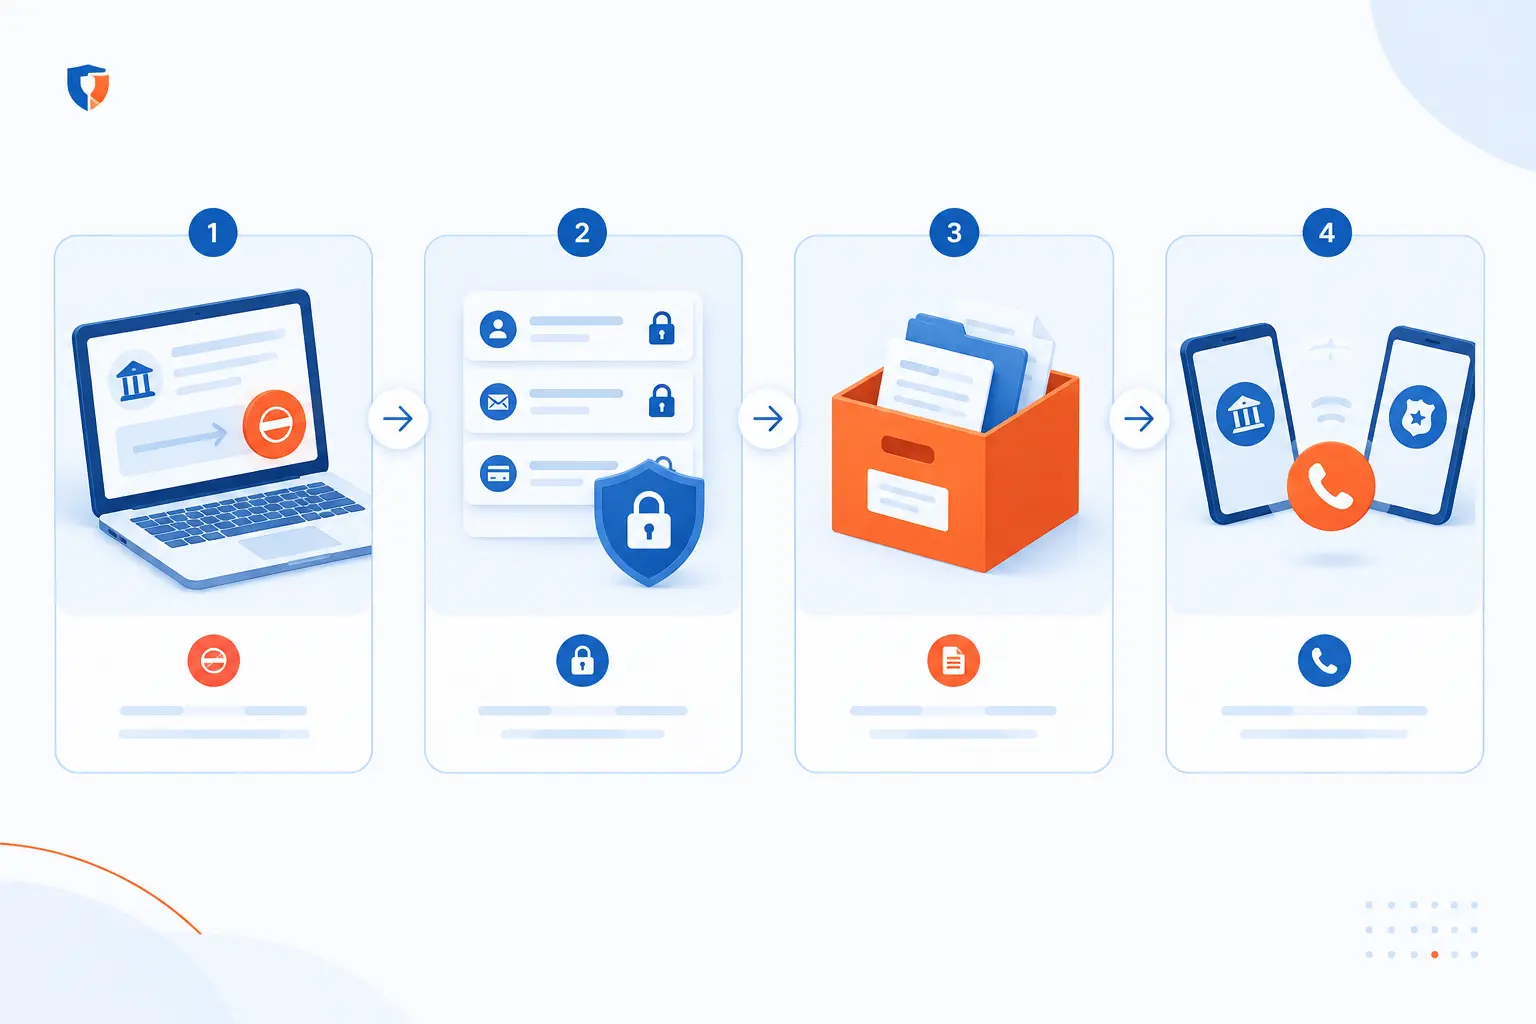
After a suspected BEC incident, act immediately to stop the payment, secure accounts, preserve evidence, and report the crime. Speed matters because banks and law enforcement may have a narrow window to freeze or recall funds. Do not wait until the full investigation is complete before contacting the bank. Treat the first hour like an emergency response window.
Contact the Bank Immediately to Recall or Freeze Funds
Contact the bank immediately and ask for a recall, hold, or freeze on the transfer. Provide the transaction amount, date, recipient bank, account number, routing number, wire reference, and any beneficiary details. If the funds moved through more than one bank, ask your institution to trace the next hop.
Then escalate internally. Notify finance leadership, legal counsel, security, and the executive owner of the affected process. Keep communication factual. The goal is to stop loss first, then investigate.
Reset Credentials and Secure Any Compromised Accounts
Reset credentials and secure compromised accounts so the attacker cannot keep reading, sending, or hiding messages. Disable affected accounts if needed, revoke active sessions, reset passwords, remove suspicious MFA methods, and review delegated access. Also inspect inbox rules, forwarding settings, signatures, and connected apps.
Do not assume the attacker is gone because the password changed. If forwarding rules remain, they may still receive copies of sensitive messages. If a malicious app remains authorized, it may continue accessing data.
Preserve Evidence and Report the Incident Quickly
Preserve evidence before deleting messages or cleaning mailboxes. Save full email headers, message bodies, attachments, login logs, payment records, bank communications, domain details, and screenshots of suspicious rules. Evidence helps banks, insurers, law enforcement, and internal investigators reconstruct what happened.
Report the incident through the FBI’s IC3 portal if you are in the United States or have a U.S. nexus, and contact local law enforcement where appropriate. The FBI advises victims to notify financial institutions, submit an IC3 complaint, contact the nearest field office, and involve local law enforcement through its public guidance. Fast reporting does not guarantee recovery, but slow reporting makes recovery harder.
FAQ
This FAQ answers the most common beginner questions about BEC in short, practical terms. The main point is simple: BEC is about tricking trusted business processes, not just tricking spam filters. If money, payroll, or confidential records are involved, verification should come before action.
What Is the Goal of Business Email Compromise
The goal of Business Email Compromise is to trick someone into sending money, changing payment instructions, or releasing sensitive data. Attackers usually target workflows where trust already exists, such as invoices, payroll, vendor payments, and executive approvals. The scam succeeds when the victim acts before verifying the request.
What Is an Example of BEC
An example of BEC is an email that appears to come from a vendor asking your accounts payable team to update bank details before paying an invoice. The invoice may be real, but the new account belongs to the attacker. Another common example is a fake CEO message asking finance to send an urgent wire transfer.
How Is BEC Done
BEC is done by researching the target, impersonating a trusted person, and sending a believable request inside a normal business workflow. The attacker may use a lookalike domain, spoofed sender, stolen mailbox, or compromised vendor account. Many attacks also use urgency or secrecy to stop the victim from checking with someone else.
What Happens If Your Email Gets Compromised
If your email gets compromised, an attacker may read messages, send fraud requests, create forwarding rules, reset other accounts, or impersonate you to coworkers and vendors. They may also search old conversations for invoices, contracts, payroll data, and customer information. The account should be secured quickly, and administrators should check for hidden rules, external forwarding, suspicious logins, and unauthorized app access.
How 1Byte Helps Reduce BEC Risk
1Byte helps reduce BEC risk by supporting the public-facing and infrastructure pieces that attackers often try to imitate or abuse. We cannot promise that hosting alone stops fraud, because BEC also depends on employee behavior and approval controls. But domain registration, SSL certificates, WordPress hosting, shared hosting, cloud hosting, cloud servers, and our role as an AWS Partner can support a cleaner, more trustworthy business presence. Our view is practical: make the real thing easier to verify and the fake thing easier to question.
Protect Brand Identity With Domain Registration and SSL Certificates
Domain registration and SSL certificates help businesses present a consistent, verifiable identity online. A well-managed domain reduces confusion around which website and email identity belong to the business. SSL certificates help visitors confirm they are connecting to the intended site over encrypted HTTPS.
For BEC prevention, this matters because attackers often rely on confusion. If customers, vendors, and staff know the correct domain, they are more likely to notice odd variations. We still recommend email authentication and monitoring, but strong domain hygiene is a sensible foundation.
Reduce Administrative Exposure With WordPress Hosting and Shared Hosting
WordPress hosting and shared hosting can reduce administrative exposure when businesses avoid improvised, unmanaged website setups. Many BEC attempts begin with public information, outdated contact pages, exposed forms, or confusing brand signals. A clear hosting environment helps teams keep public business information accurate.
Accuracy matters more than many teams think. If an attacker can copy old staff names, outdated finance contacts, or abandoned domains, they gain material for impersonation. We see hosting as part of the trust surface, not just a place where pages live.
Strengthen Business Operations With Cloud Hosting and Cloud Servers
Cloud hosting and cloud servers help businesses place important systems in structured environments instead of ad hoc infrastructure. That matters for BEC because payment portals, customer sites, internal tools, and business applications need consistent access control and administrative discipline. As an AWS Partner, 1Byte can connect cloud infrastructure conversations to practical risk reduction.
This does not replace finance approval rules or employee training. It supports them. When systems are organized, access is easier to review, ownership is clearer, and suspicious changes are less likely to be ignored.


Conclusion
Business Email Compromise is dangerous because it hides inside ordinary work. It does not need a dramatic hack if a believable email can redirect a payment, change payroll, or expose private records. The strongest defense is a mix of verification habits, email authentication, MFA, dual approval, mailbox monitoring, and fast incident response.
We believe the healthiest security culture is one where people are allowed to pause. A finance employee should feel safe asking, “Can we verify this first?” A payroll specialist should have a process that backs them up. An executive should welcome a confirmation call.
If your business handles invoices, wires, payroll, or vendor bank details, start with one next step: document exactly how payment changes are verified. Then test that process with your team before an attacker does.