
- What Is SASE? A Cloud-Based Model That Unifies Networking and Security
- Why the Model Emerged in Modern Enterprise Networks
- How the Architecture Works Across Users, Apps, and Sites
- Core Components in a Unified Platform
- The Main Benefits for Distributed Organizations
- Common Use Cases and Deployment Priorities
- SASE vs SD-WAN, SSE, and VPN
- How to Evaluate a SASE Platform
- Frequently Asked Questions
- How 1Byte Supports Secure Website and Cloud Infrastructure
- Conclusion
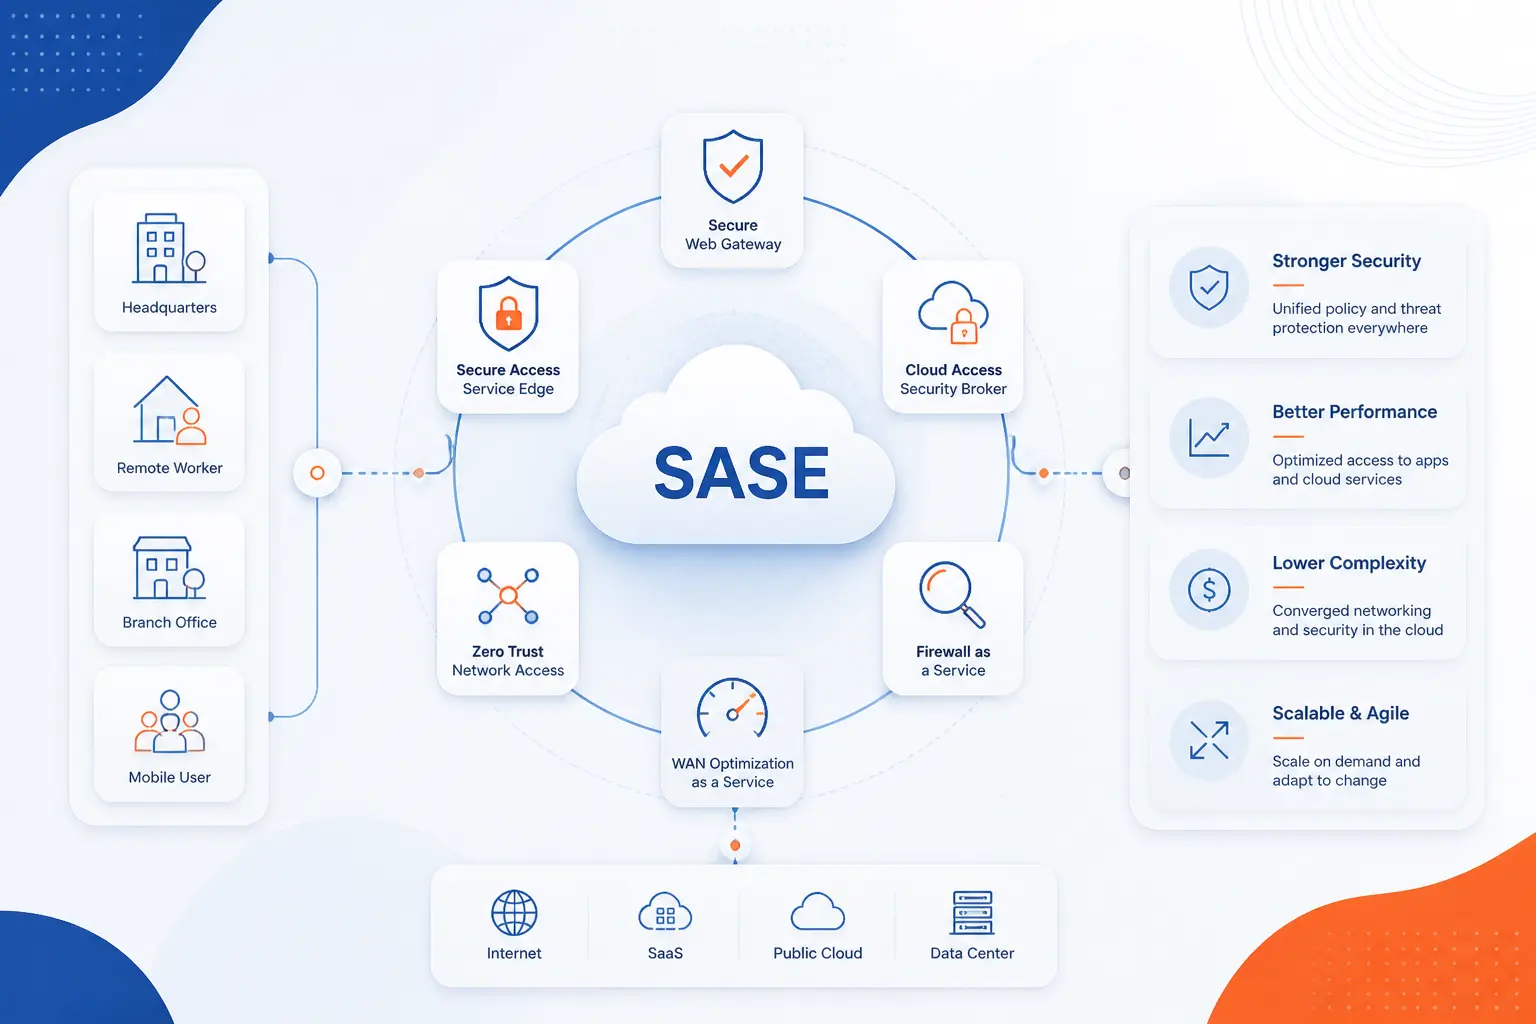
SASE is a cloud-based model that brings wide area networking and security together in one architecture. Instead of sending every user and branch through a corporate data center, SASE applies security controls close to the user, the application, and the data. That matters because work now happens across SaaS apps, public cloud, branch offices, home networks, and mobile devices. At 1Byte, we see SASE as a practical response to a simple problem: the old network edge is no longer one place.
The idea is easy to grasp once we stop treating networking and security as separate lanes. SASE connects users to resources through identity-aware policies, secure traffic inspection, and optimized routing. It can include SD-WAN, Zero Trust Network Access, secure web gateway, CASB, DLP, firewall-as-a-service, and related controls. The goal is not to buy a shiny label. The goal is to make access safer, simpler, and more consistent wherever work happens.
What Is SASE? A Cloud-Based Model That Unifies Networking and Security
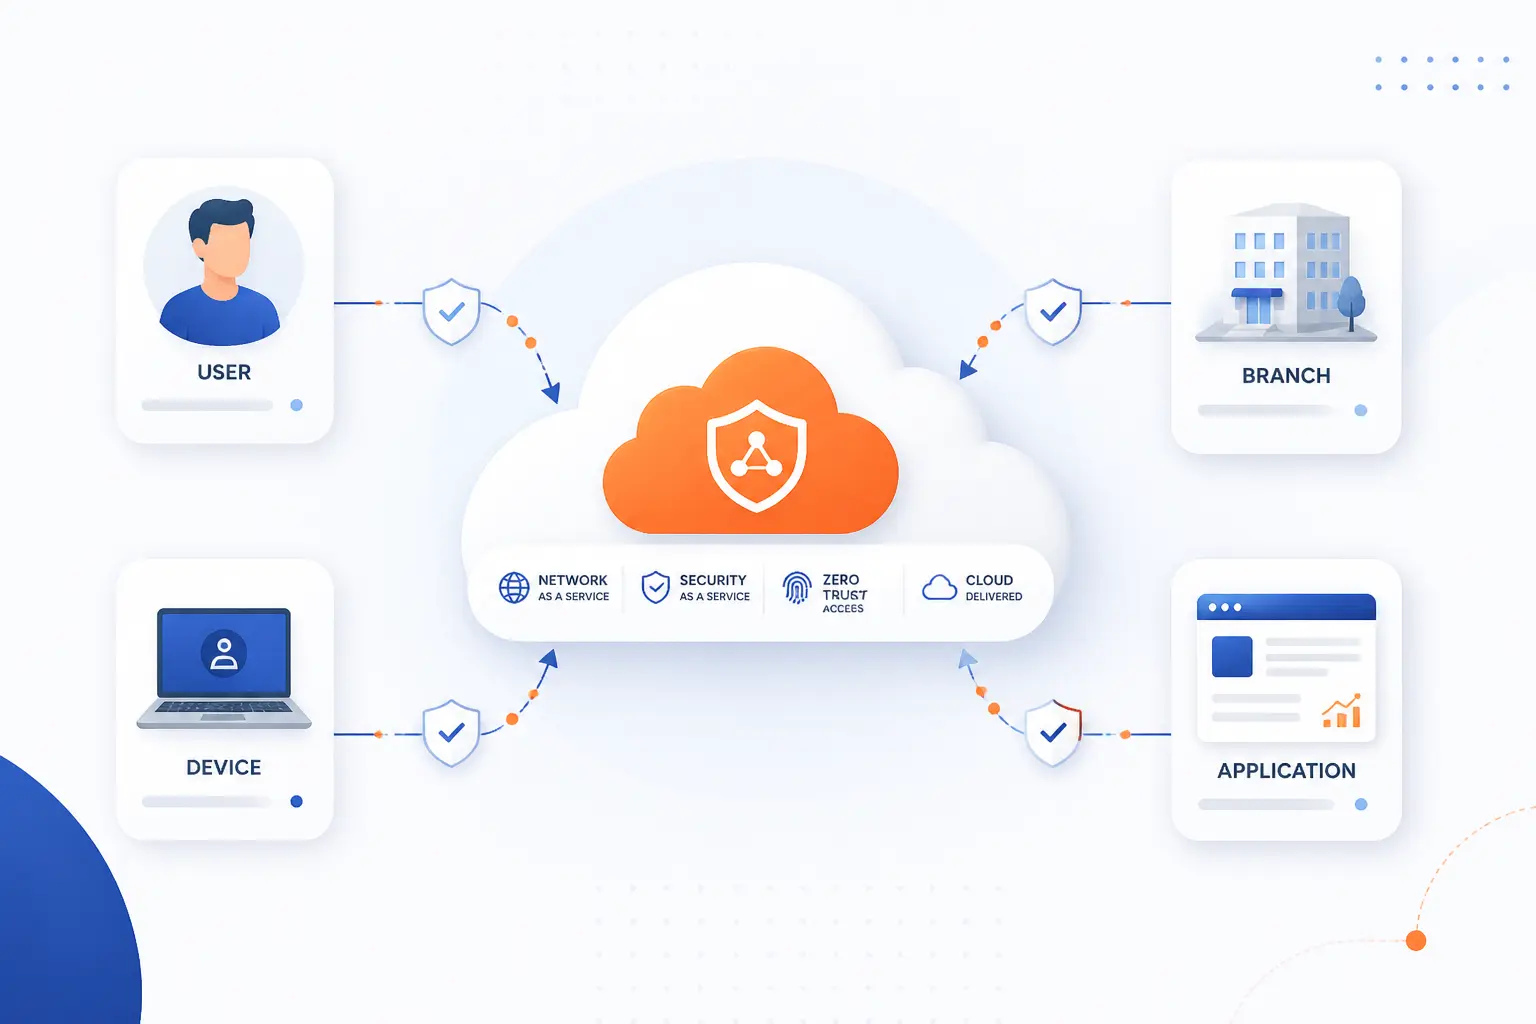
SASE is an architecture that combines network connectivity and security services into a cloud-delivered model. It gives users, branches, devices, and applications secure access based on identity, policy, context, and risk. Rather than trusting traffic because it comes from a corporate network, SASE checks who is asking, what device they use, where they are, and what they need to reach. In our view, the strongest part of SASE is this shift from “connect first, secure later” to “verify, inspect, and route intelligently.”
The term stands for Secure Access Service Edge. “Secure access” points to identity-based controls and traffic inspection. “Service edge” means those controls are delivered from distributed cloud locations instead of one central appliance stack. This is why SASE fits companies with SaaS apps, remote staff, public cloud workloads, and many sites.
A simple example helps. A salesperson opens a CRM app from a hotel Wi-Fi network. With a traditional VPN model, traffic may hairpin through headquarters before reaching the app. With SASE, access can be authenticated, checked against policy, inspected for threats, and routed through a nearby service point. The user gets the app, but not broad access to the whole private network.
FURTHER READING: |
| 1. What Is Penetration Testing and How Does It Work |
| 2. What Is a Botnet? How It Works and Why It Matters |
| 3. What Is the OSI Model? Layers, Purpose, and Uses |
Why the Model Emerged in Modern Enterprise Networks
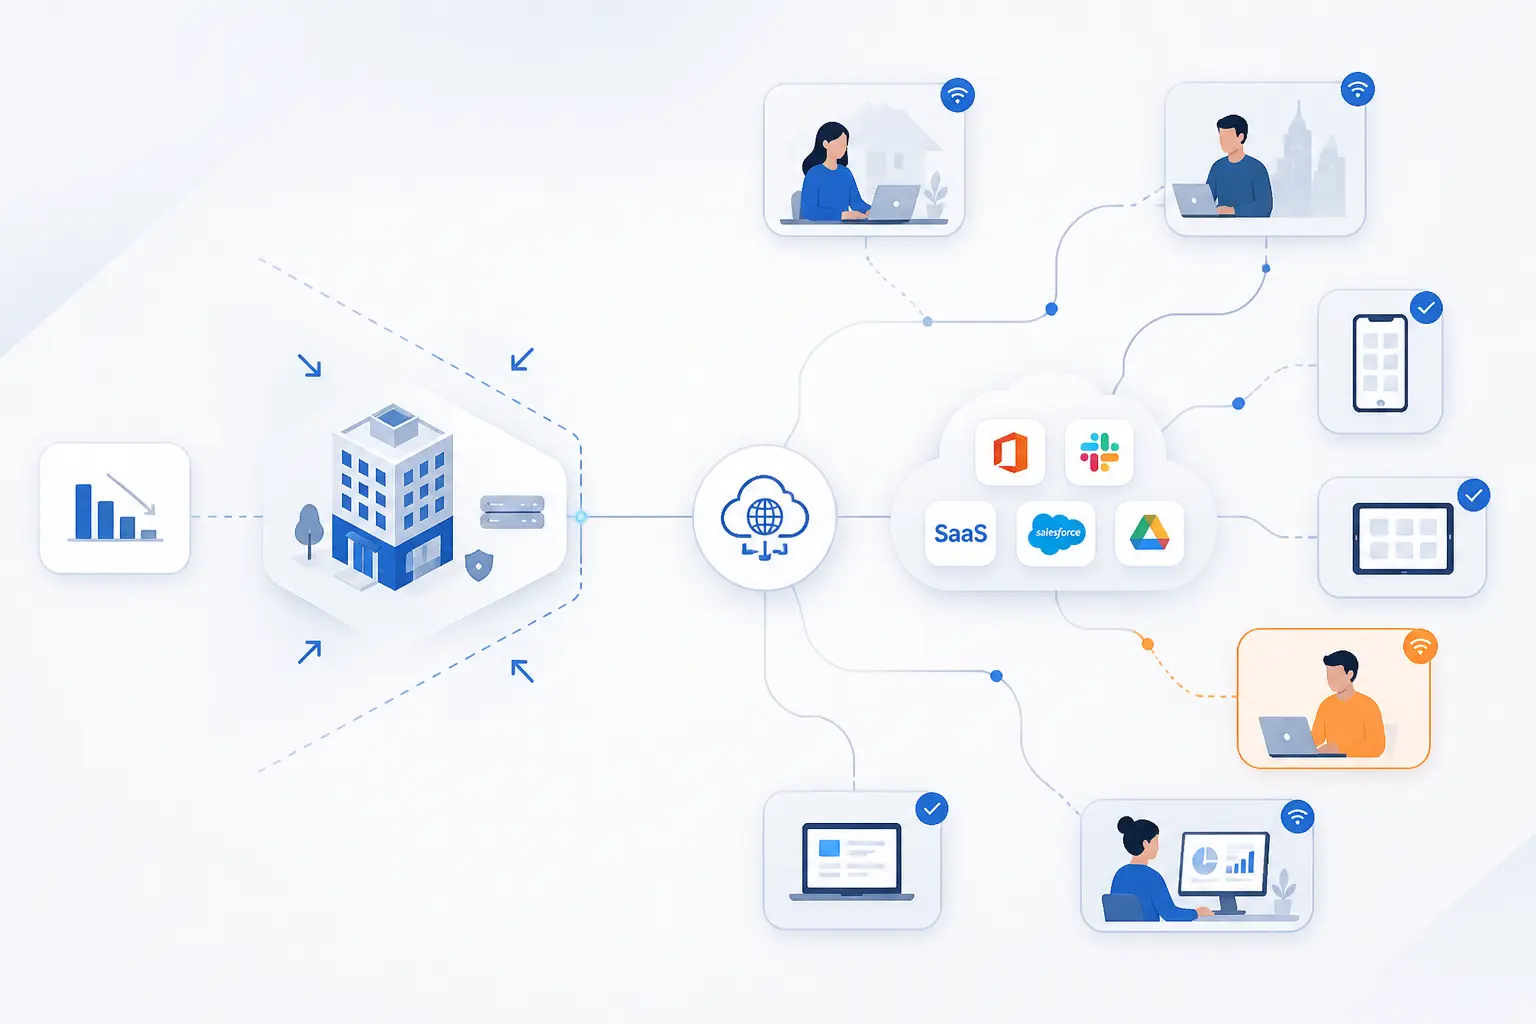
SASE emerged because enterprise traffic stopped living inside one protected office network. Applications moved to SaaS and public cloud, users moved beyond fixed offices, and devices multiplied. Security teams then had to protect more access paths with tools that were designed for a smaller world. Public cloud spending was forecast to reach $723.4 billion in 2025, which shows how far business systems have shifted away from privately owned infrastructure.
Cloud Adoption Moved Apps and Data Beyond the Corporate Perimeter
Cloud adoption made the old perimeter less useful because important apps and data now sit outside company-owned buildings. Many employees reach Microsoft 365, Salesforce, GitHub, hosted databases, and cloud dashboards directly over the internet. Backhauling that traffic through a central data center can add delay and create blind spots.
SASE answers this by moving inspection and access control closer to where traffic already goes. It treats the internet as the main transport path, then wraps that path with identity, policy, encryption, and threat controls. We like this model because it accepts reality. The cloud is not a side road anymore. For many organizations, it is the main road.
Remote Work, Mobile Access, and BYOD Expanded the Edge
Remote work and personal devices expanded the network edge to homes, airports, cafes, phones, and tablets. U.S. labor research reported that 22.7 percent of employed persons did at least some paid work hours from home in February 2024. That is not a temporary footnote for security teams. It changes where trust decisions must happen.
Bring-your-own-device and bring-your-own-app habits add another layer. The Microsoft and LinkedIn 2024 Work Trend Index found that 78% of AI users brought their own AI tools to work. We mention that because unsanctioned tools are a real access and data problem. SASE does not magically control every personal choice, but it can give organizations better policy enforcement at the access layer.
Point Products and MPLS Increased Cost and Complexity
Point products and MPLS-heavy designs became hard to manage because each site, tool, and traffic path needed separate attention. A company might run one appliance for web filtering, another for firewalling, another for VPN, another for data loss prevention, and a separate WAN contract for branch routing. That patchwork can work for a while. Then mergers, cloud projects, and remote work expose every seam.
SASE reduces that sprawl by bringing key controls into one policy model. It does not mean every company must rip and replace everything overnight. We usually prefer phased adoption. Start with the pain point that is costing the most time, such as remote access or branch internet breakout, then expand from there.
How the Architecture Works Across Users, Apps, and Sites
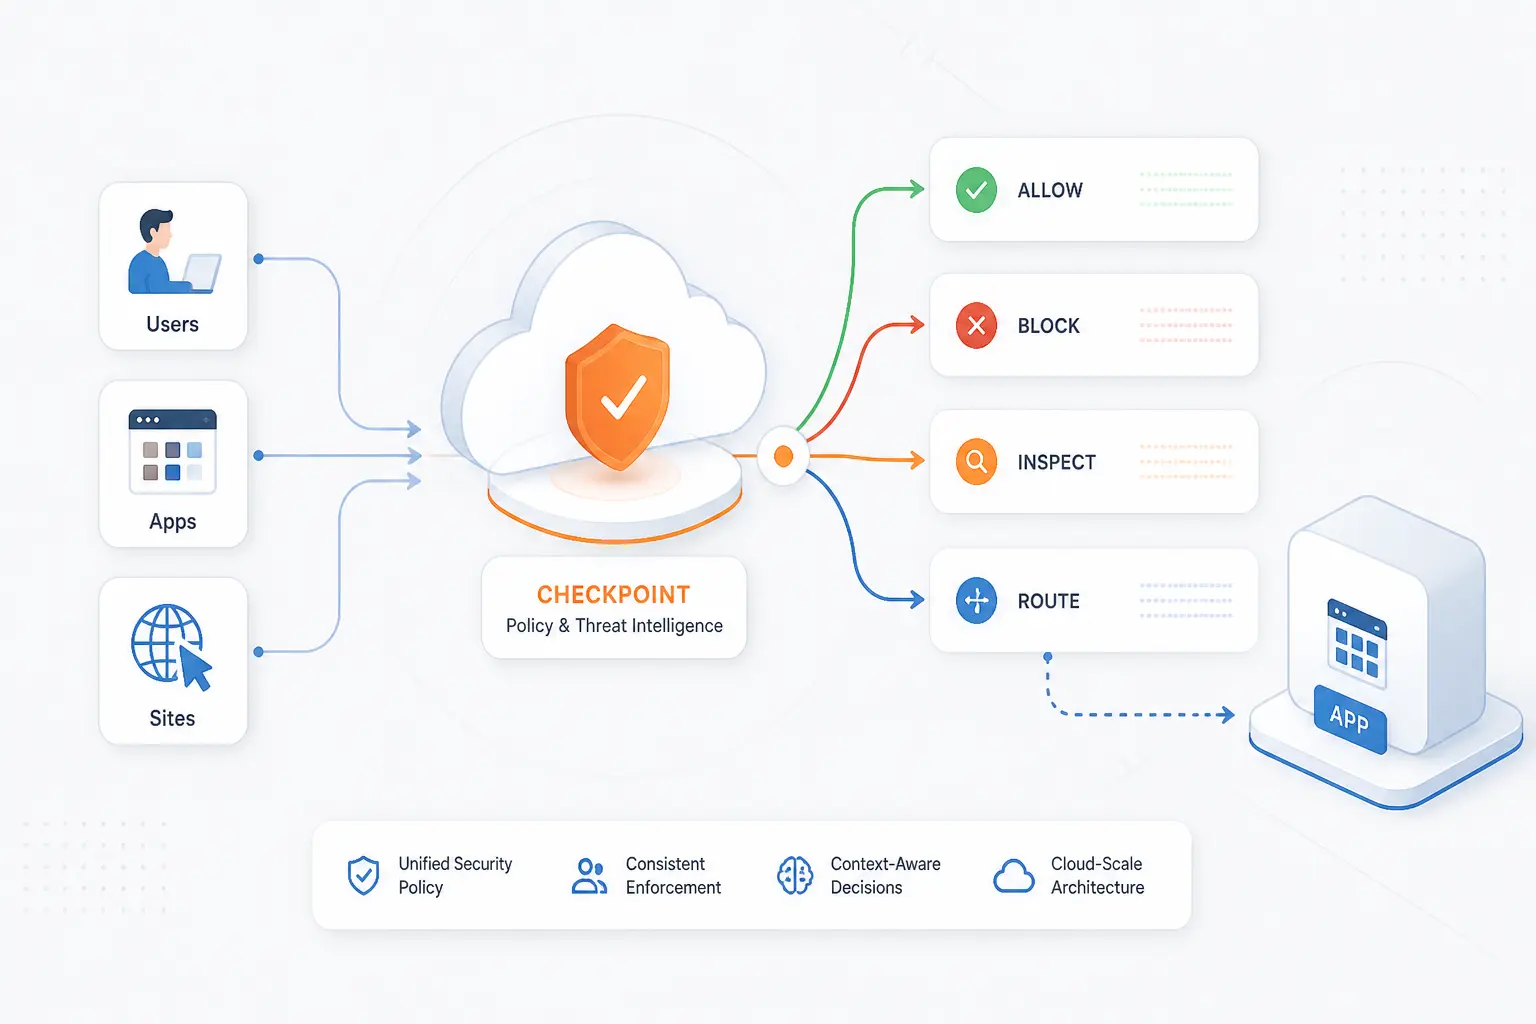
SASE works by steering traffic through cloud-delivered security and networking services before users reach applications or data. The platform checks identity, device posture, location, application sensitivity, and policy. It then decides whether to allow, block, inspect, limit, or route traffic along a better path. The mechanics matter because SASE is not one box. It is a coordinated architecture for many edges.
Identity-Driven Access Policies
Identity is the control point that tells SASE who should access what. A finance employee may need payroll access, but not engineering repositories. A contractor may need one project portal, but not the full corporate network. That is the heart of the model.
Good SASE policy uses more than a username and password. It can consider multi-factor authentication, role, group, device health, location, time, and application risk. This lines up with zero trust thinking, where access is granted per session and evaluated continuously. NIST describes zero trust through concepts such as a policy engine and policy administrator in its technical publication.
Cloud-Native Delivery Through Distributed Points of Presence
Distributed points of presence let SASE inspect and route traffic close to users instead of forcing every request through headquarters. If an employee in New York, Singapore, or Paris reaches a SaaS app, the nearest service edge can apply policy and forward traffic. That can reduce unnecessary detours.
The design is similar to how content delivery networks improved web performance, but with security controls added. The service edge becomes the place where authentication, encryption, filtering, logging, and routing decisions happen. In practice, the quality of those locations matters. A poor global footprint can turn a promising SASE project into a slow one.
Support for Branches, Data Centers, Cloud Resources, and Remote Users
SASE supports many access patterns because modern organizations have more than one kind of edge. A branch office may use SD-WAN. A remote employee may use a lightweight client. A cloud workload may connect through tunnels or routing integrations. A private application may be published through zero trust access rather than exposed through a full VPN.
This flexibility is one reason SASE gets boardroom attention. It can cover a retailer with many stores, a software company with remote engineers, or a manufacturer with plant networks and cloud analytics. The details differ, but the pattern is the same. Connect the edge, verify access, inspect traffic, and enforce policy consistently.
Centralized Policy Enforcement Across Every Edge
Centralized policy enforcement means administrators define rules once and apply them across users, sites, apps, and traffic paths. Without that, teams end up copying firewall rules, VPN groups, and web policies across many systems. That creates mistakes.
In a SASE model, the security team can create a policy like “marketing users may access approved SaaS apps from managed devices” and apply it broadly. The networking team can also steer latency-sensitive traffic differently from bulk downloads. We value this because consistency is underrated. Many incidents begin with one forgotten exception.
Core Components in a Unified Platform
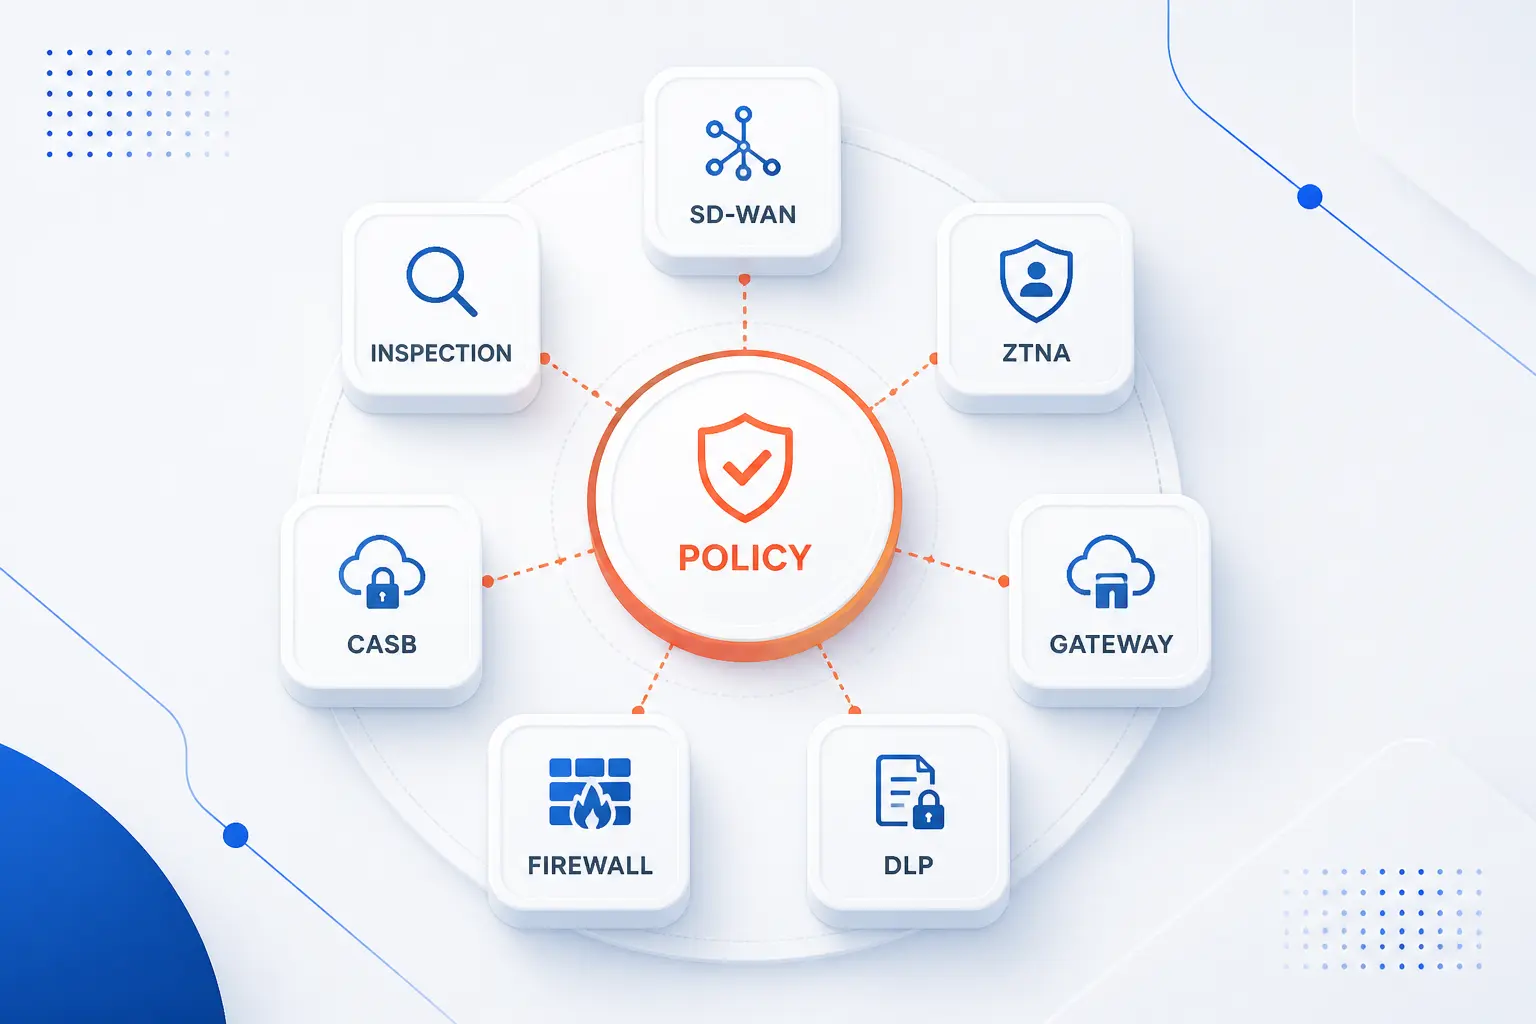
A SASE platform usually combines networking and security functions that used to be bought and operated separately. The exact mix varies by vendor and maturity level, but the common building blocks are SD-WAN, ZTNA, secure web gateway, CASB, DLP, firewall-as-a-service, and next-generation firewall features. These parts should share policy context. If they do not, the platform may be a bundle rather than a true architecture.
| Component | Primary job | Practical example |
|---|---|---|
| SD-WAN | Routes branch and site traffic across available links | Use broadband and backup links for a store network |
| ZTNA | Grants private app access by identity and context | Let contractors reach one internal portal |
| Secure Web Gateway | Inspects web traffic and blocks risky destinations | Stop access to malicious download sites |
| CASB and DLP | Controls cloud app use and protects sensitive data | Block uploads of customer records to unsanctioned apps |
| FWaaS and NGFW | Applies firewall policy from the cloud | Filter traffic between users, sites, and cloud apps |
SD-WAN
SD-WAN is the networking layer that chooses how traffic moves between branches, users, data centers, and cloud services. It can use multiple underlay connections, such as broadband, LTE, fiber, or private circuits. Then it applies business policy to decide where traffic should go.
For example, video calls may need a cleaner path than a software update. Payment traffic may need strict segmentation. The MEF standard for SD-WAN defines service behavior from the subscriber’s view, including externally visible behavior. In SASE, SD-WAN gives the architecture its traffic steering muscles.
Zero Trust Network Access
Zero Trust Network Access gives users access to specific applications, not broad access to a whole network. That is a major improvement over traditional VPN habits. A user should not see every internal subnet just because they passed one login prompt.
ZTNA checks identity, device posture, and context before allowing access. It can also hide private applications from the open internet. We see ZTNA as one of the most practical first steps toward SASE because it solves a common problem quickly. Replace oversized remote access with narrower, policy-based access.
Secure Web Gateway
A secure web gateway protects users as they browse the web and access internet services. It can block malicious sites, inspect downloads, enforce acceptable-use policy, and apply controls to encrypted traffic where permitted. This matters because many attacks still begin with a link, file, or fake login page.
In a SASE platform, the secure web gateway should understand user identity and device context. A managed laptop on a trusted network may receive different treatment from an unmanaged personal device. That does not mean users get a free pass. It means the policy can match the risk.
Cloud Access Security Broker and Data Loss Prevention
CASB and DLP help control how users handle data in cloud applications. CASB focuses on visibility and policy enforcement for cloud app usage. DLP focuses on detecting and preventing sensitive data from leaving approved places.
For example, a CASB may flag an unsanctioned file-sharing app. DLP may stop a spreadsheet containing customer records from being uploaded there. The Cloud Security Alliance glossary includes both CASB and DLP among data security terms in its reference material. In SASE, these tools make cloud access less of a blind leap.
Firewall-as-a-Service and Next-Generation Firewall Capabilities
Firewall-as-a-service delivers firewall controls from the cloud rather than from hardware at every site. Next-generation firewall capabilities usually add application awareness, intrusion prevention, user-based rules, and deeper traffic inspection. Together, they give distributed organizations a way to apply firewall policy across many locations.
This is useful when branches use local internet breakout. Instead of buying and managing large appliances for every office, traffic can be sent through cloud firewall controls. We still believe architecture comes first. FWaaS is valuable when policies, logs, routing, and identity fit the broader SASE design.
The Main Benefits for Distributed Organizations
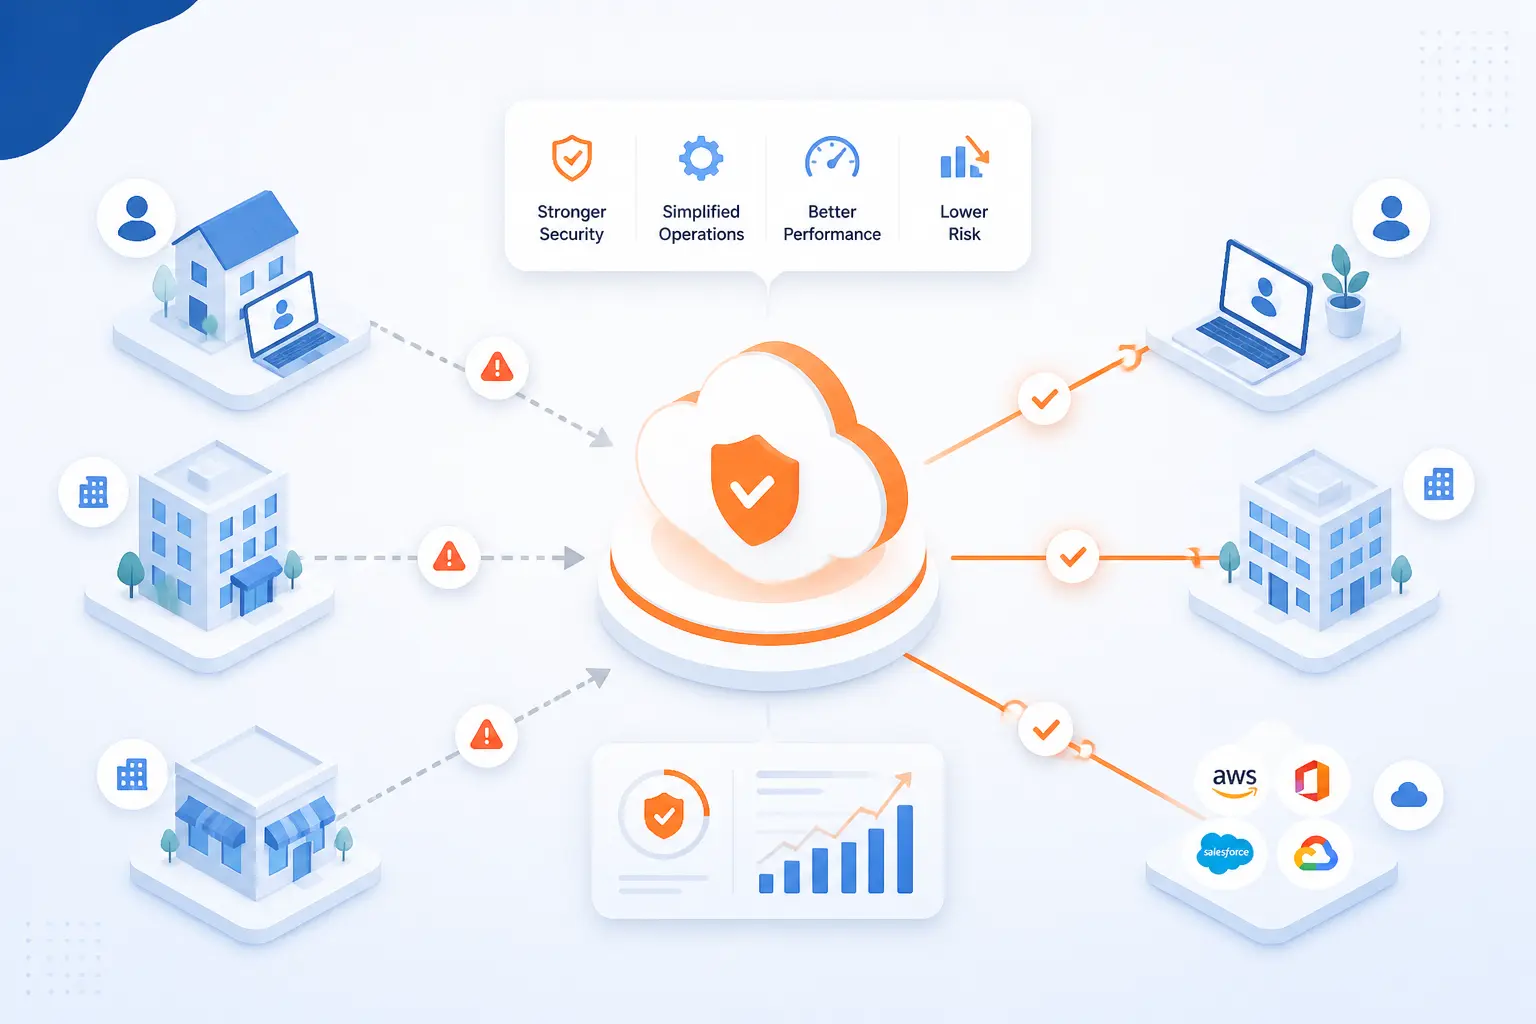
SASE benefits distributed organizations by reducing the gap between where people work and where security controls operate. It can improve risk management, simplify operations, shorten traffic paths, and make policy more consistent. The value is strongest when a company has remote users, branch sites, cloud apps, and sensitive data spread across many locations. We would not call it a cure-all. We would call it a cleaner operating model for a messy network world.
Stronger Security and Lower Cyber Risk
SASE can lower cyber risk by applying identity-based access, inspection, and data controls across more traffic paths. A user gets the access they need, not an open doorway into everything. Suspicious web traffic can be blocked. Sensitive data movement can be watched more closely.
The financial stakes are real. The 2025 breach study reported a global average cost of $4.44 million. SASE will not prevent every incident, and anyone promising that is selling fairy dust. But it can reduce common exposure points, especially around remote access, web threats, and unmanaged cloud activity.
Lower Complexity and Lower Total Cost of Ownership
SASE can reduce complexity by replacing scattered appliances and policies with a unified service model. Teams spend less effort maintaining different rule sets across VPN gateways, branch firewalls, web filters, and cloud security tools. That can reduce operational drag.
Total cost of ownership depends on the starting point. A company locked into heavy MPLS contracts may save money through internet-based SD-WAN. Another company may spend first because it needs migration help, policy cleanup, or identity improvements. Our opinion is simple: SASE works best when the business case includes operations, risk, and user experience, not license cost alone.
Better Performance and User Experience
SASE can improve performance by avoiding unnecessary backhaul and choosing better paths to cloud apps. If a user sits far from headquarters but close to the SaaS provider, routing through headquarters makes little sense. A nearby service edge can be faster and cleaner.
User experience also improves when access feels natural. Employees should not have to launch a heavy VPN just to open one approved app. Branch sites should not suffer because every cloud request takes a scenic route. Good SASE design removes detours while keeping controls in place.
More Visibility and Consistent Policy Enforcement
SASE improves visibility by collecting access, traffic, threat, and policy data across many edges. That gives security teams a better view of who accessed what, from where, and under which conditions. It also makes investigations easier.
Consistency is just as valuable. If remote users follow one policy and branch users follow another, gaps appear. SASE helps close those gaps by tying enforcement to identity and context. The result is fewer surprises, which is exactly what security teams want.
Scalability for Growth, Change, and Hybrid Work
SASE supports growth because new users, sites, and cloud services can be added under a common access model. A company opening new branches should not need a fresh appliance design each time. A company hiring remote staff should not need to stretch old VPN concentrators forever.
This does not remove planning. Identity design, routing, logging, and data rules still need care. Yet the architecture is better suited for change than a rigid perimeter model. We have learned that infrastructure should bend with the business, not snap every time the org chart changes.
Common Use Cases and Deployment Priorities
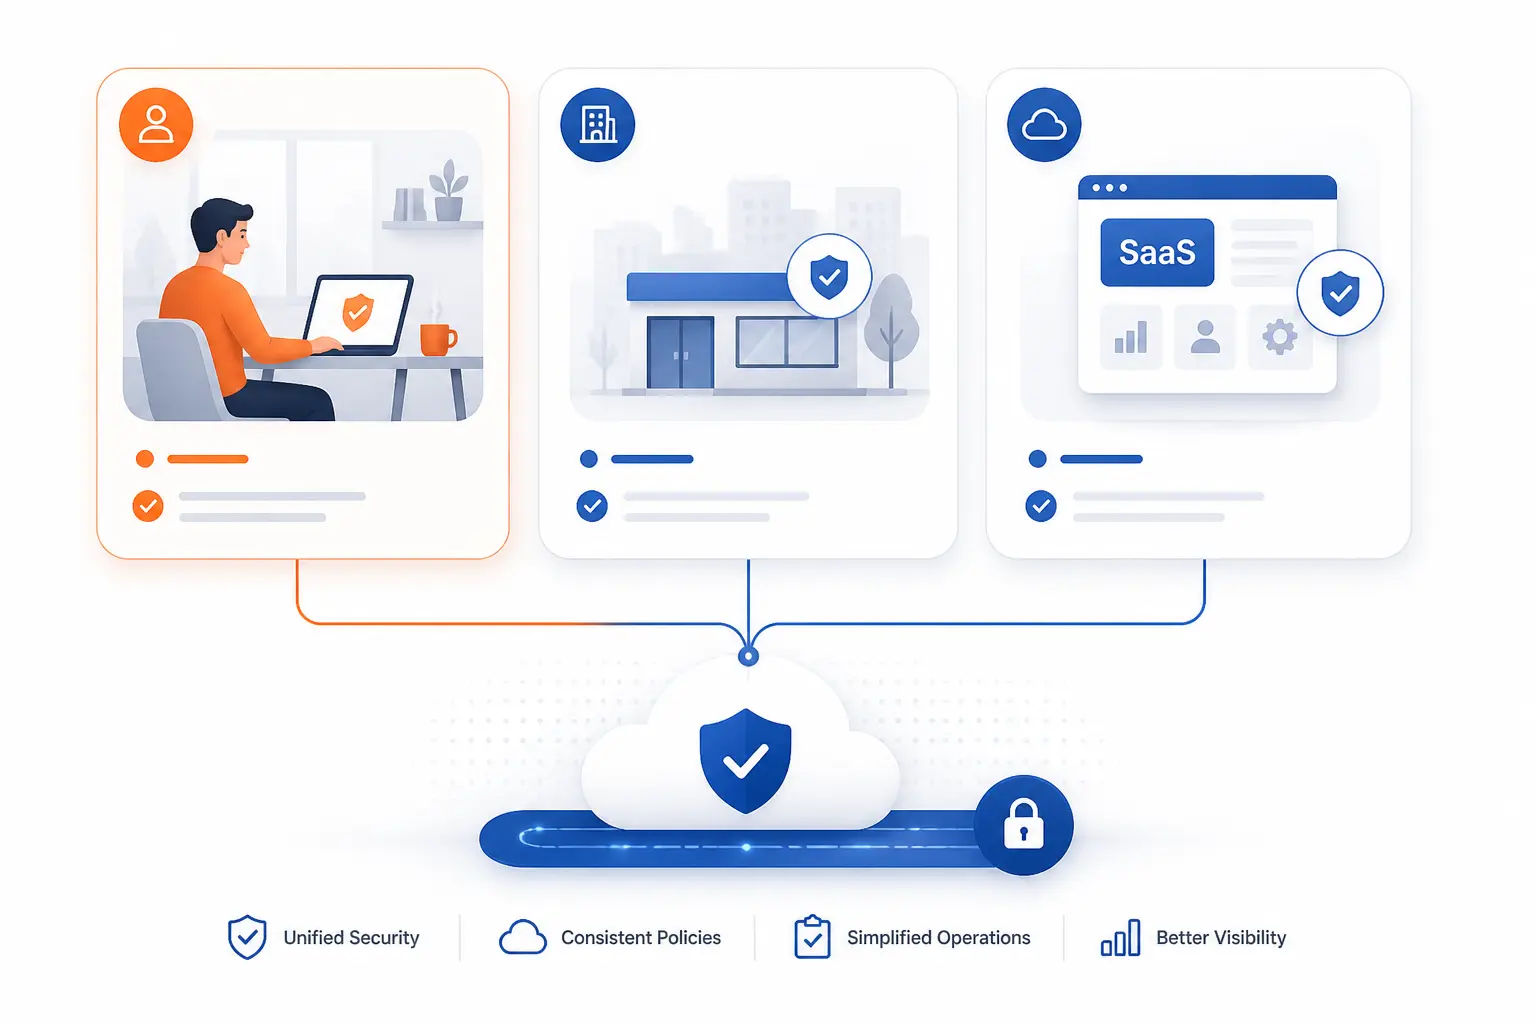
SASE is most useful when access and security problems cross locations, devices, and cloud services. Common starting points include hybrid work, branch connectivity, SaaS governance, and WAN modernization. The best priority is usually the one with the clearest pain and measurable risk. Do not start with the largest diagram. Start where users, admins, and auditors already feel the friction.
| Use case | Best first move | Why it matters |
|---|---|---|
| Hybrid workforce | Replace broad VPN access with ZTNA | Limits user access to approved apps |
| Distributed sites | Deploy SD-WAN with cloud security inspection | Improves branch routing and policy control |
| Cloud and SaaS | Add CASB and DLP policies | Reduces risky data movement |
| WAN modernization | Reduce unnecessary MPLS dependence | Supports internet-first cloud access |
Hybrid Workforces and Secure Remote Access
Hybrid workforces often use SASE first to replace broad VPN access with identity-based access. This is a practical move because VPN pain is easy to spot. Users complain about slow connections. Admins worry about over-permissioned access. Security teams see unmanaged networks everywhere.
ZTNA, secure web gateway, and cloud firewall controls can create a safer remote access pattern. A remote accountant can reach the finance app. A developer can reach the needed repository. Neither should automatically see every internal system. That is the kind of boring security win we like.
Branch, Retail, and Distributed Site Connectivity
Branches and distributed sites use SASE to combine smarter routing with cloud-delivered security. A retailer, for example, may need store systems, guest Wi-Fi separation, payment traffic protection, and SaaS access. Running all traffic back to headquarters can be slow and expensive.
SD-WAN helps choose paths across available links. Security services inspect internet-bound and private traffic according to policy. The branch gets simpler connectivity without becoming a soft target. That balance is the point.
Cloud and SaaS Access With Better Data Protection
Cloud and SaaS access use cases focus on visibility, app control, and data protection. Employees may use approved SaaS tools, unsanctioned tools, browser extensions, AI assistants, and personal storage. The security issue is not only access. It is what happens to data after access is granted.
CASB and DLP policies can detect risky uploads, sensitive content, unusual sharing, and suspicious app behavior. Secure web gateway controls can reduce exposure to phishing and malware. SASE brings those checks closer to normal work, which makes enforcement more realistic.
MPLS Migration and WAN Modernization
MPLS migration uses SASE to shift from private-circuit-first networking toward policy-based internet and cloud access. Many organizations still keep some private links where they make sense. The change is that MPLS is no longer the default answer for every branch and workload.
SD-WAN can use broadband, wireless, and private circuits together. SASE security services then inspect and control traffic as it leaves the site. This lets companies modernize the WAN without pretending the internet is automatically safe. It is useful transport, but it needs policy wrapped around it.
SASE vs SD-WAN, SSE, and VPN
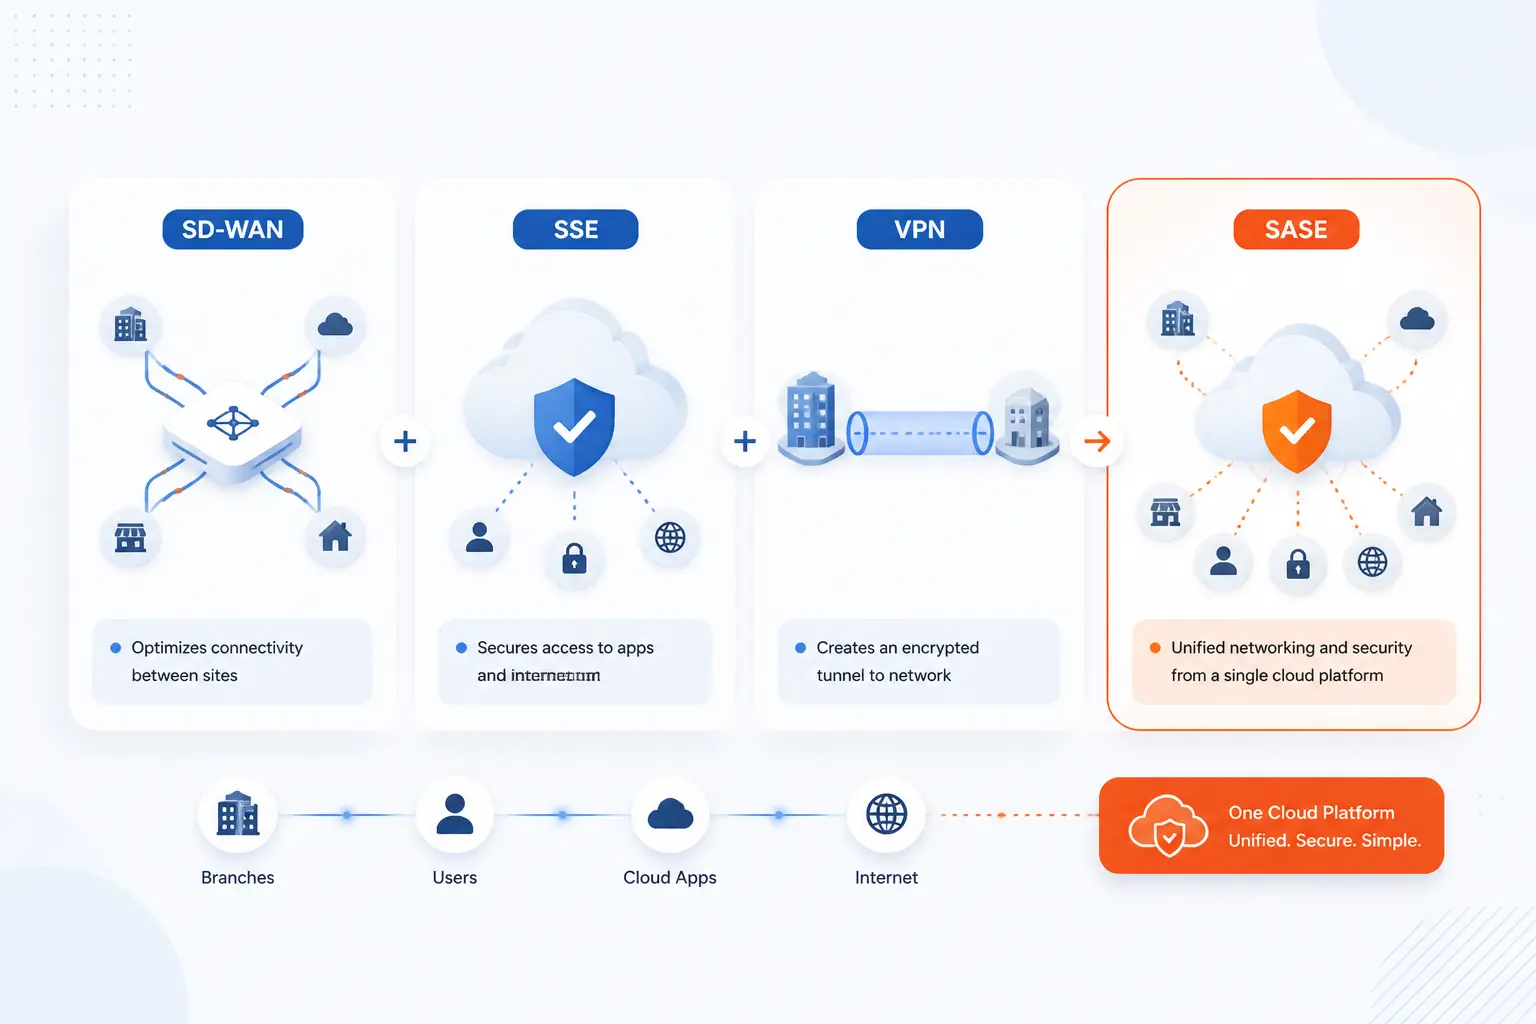
SASE is broader than SD-WAN, broader than VPN, and closely related to SSE. SD-WAN focuses on traffic routing and WAN connectivity. SSE focuses on cloud-delivered security services. VPN focuses on encrypted tunnels, usually for remote access. SASE combines networking and security into one coordinated model.
| Model | Main focus | Best fit | Limitation alone |
|---|---|---|---|
| SASE | Networking plus security | Distributed users, sites, and cloud apps | Requires planning across teams |
| SD-WAN | WAN routing | Branch connectivity | Needs security services around it |
| SSE | Security service edge | Web, SaaS, and private app security | Does not fully cover WAN routing |
| VPN | Encrypted tunnel access | Simple remote connectivity | Often grants too much network reach |
SASE vs SD-WAN
SASE includes SD-WAN-style connectivity, while SD-WAN alone does not include the full security stack. SD-WAN is excellent at steering traffic between sites and cloud services. It can improve branch performance and reduce dependence on private circuits.
The problem appears when SD-WAN is deployed without strong security controls. Direct internet breakout can help performance, but it can also expose users and sites. SASE wraps SD-WAN with security services such as ZTNA, secure web gateway, CASB, DLP, and firewall policy. We see SD-WAN as the road system. SASE adds the checkpoints, signs, and rules of the road.
SASE vs SSE
SSE is the security half of SASE without the full WAN networking side. It usually includes secure web gateway, CASB, ZTNA, DLP, and firewall-related controls. SSE is useful when an organization wants to secure users and cloud access but is not ready to change the WAN.
SASE goes further by adding WAN connectivity and traffic optimization into the same strategy. Some companies start with SSE, then add SD-WAN later. Others start with SD-WAN and add SSE controls. Both paths can work if the end state is clear.
SASE vs VPN
SASE is more granular than VPN because it grants access to specific resources based on policy instead of extending a user onto the network. VPN still has a place for some administrative and legacy use cases. It is familiar, widely supported, and simple to understand.
But VPN was not designed for a world where every user, device, and app needs separate trust decisions. A compromised VPN account can create broad exposure. ZTNA within SASE narrows that exposure by giving users access to what they need. Less reach means less blast radius.
How to Evaluate a SASE Platform
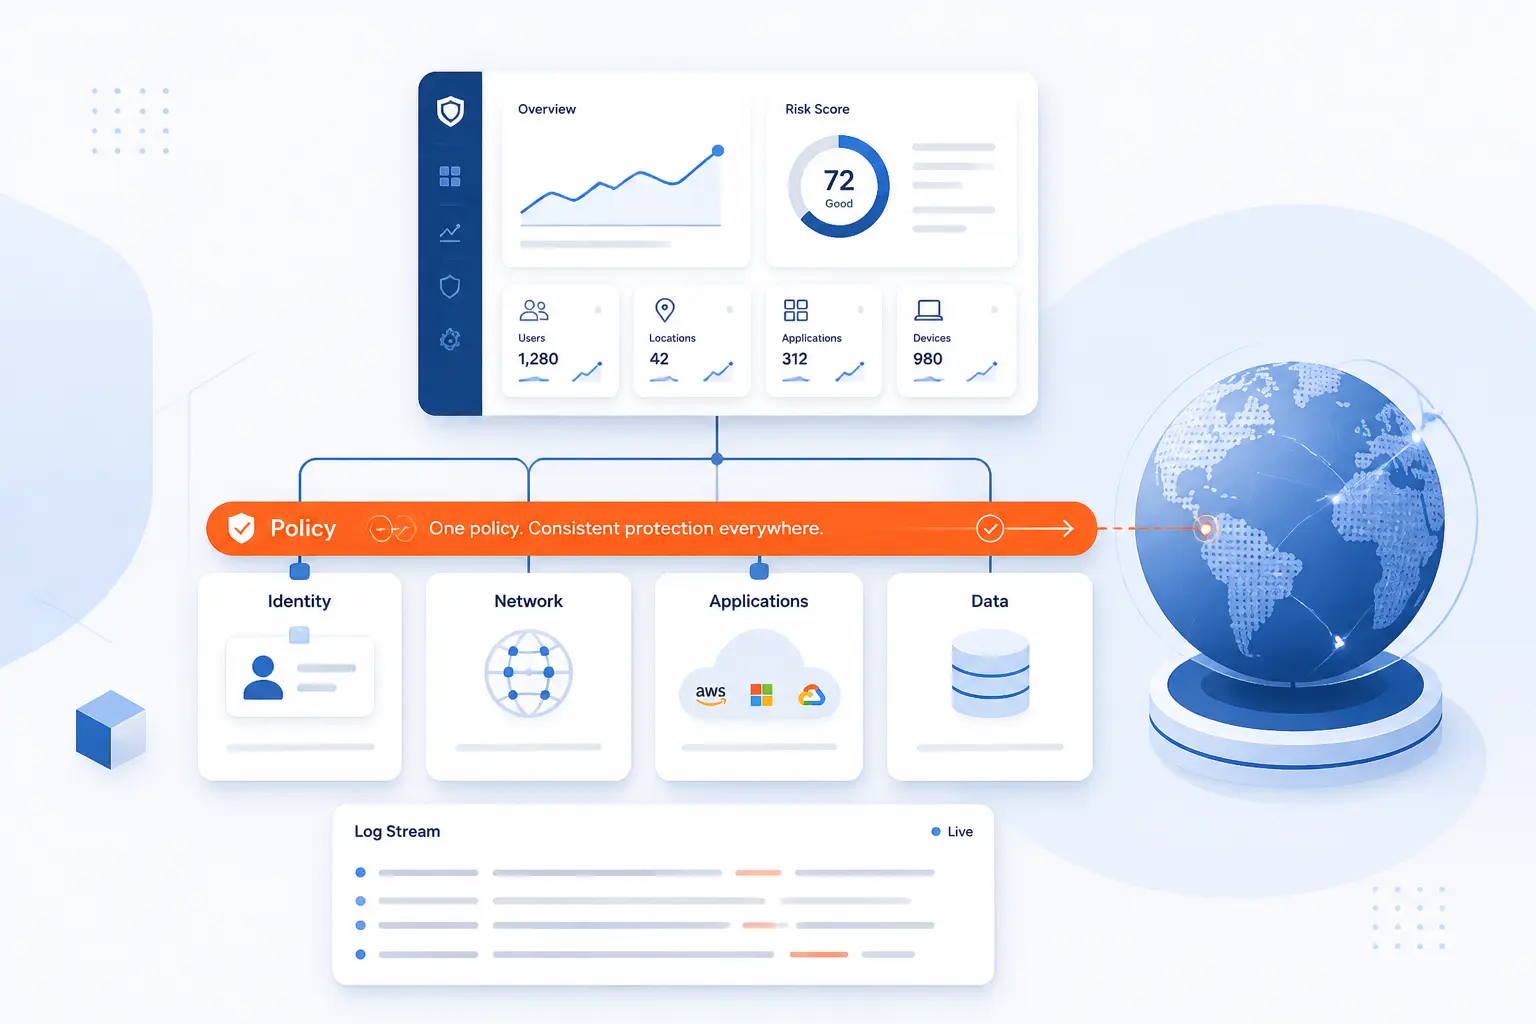
To evaluate a SASE platform, look for integrated policy, strong identity controls, real traffic inspection, global delivery quality, and operational simplicity. Do not stop at a feature checklist. Ask how the pieces share context, how logs are correlated, and how policies are enforced across remote users, branches, cloud resources, and private apps. CISA’s maturity model organizes zero trust work around identity, devices, networks, applications, workloads, and data, which is a useful lens for evaluation.
Prioritize a Truly Integrated Service
A truly integrated SASE service shares identity, policy, logging, and enforcement across networking and security functions. If each module has its own console, policy language, and log format, the operational burden remains. That is tool consolidation in name only.
Ask direct questions during evaluation. Can one policy affect web access, private app access, and branch traffic? Can logs show a user’s full path across services? Can administrators update rules without touching many systems? The answers reveal whether the platform is unified or just packaged together.
Check Global Reach, Points of Presence, and Latency
Global reach matters because SASE performance depends on where traffic enters the provider’s service edge. A remote user should not be forced to cross a continent before policy inspection begins. A branch should have a nearby path for cloud-bound traffic.
Ask providers for latency data in the regions where your users actually work. Test from real locations, not just headquarters. Include mobile users, home users, branch sites, and cloud workloads. We trust pilot results more than polished maps.
Verify Zero Trust, Scalability, and Policy Consistency
Zero trust controls should verify every access request with identity, device, context, and least privilege. That means SASE evaluation must include your identity provider, endpoint posture checks, app segmentation, and policy design. Do not treat zero trust as a checkbox.
Scalability also needs proof. Can the platform handle new branches, acquisitions, contractors, and cloud regions without a maze of exceptions? Policy consistency is where many projects stumble. We recommend testing common cases and awkward cases because real networks always have both.
Frequently Asked Questions
SASE questions usually come from readers trying to separate the architecture from nearby terms. The short answer is that SASE combines networking and security, while related models handle smaller parts of that picture. These quick answers should help you place each term correctly.
What Does SASE Stand For?
SASE stands for Secure Access Service Edge. It describes a cloud-delivered architecture that combines secure access controls with network connectivity. The name is technical, but the idea is straightforward: apply security and routing close to users and applications.
Does SASE Include SD-WAN?
Yes, SASE commonly includes SD-WAN as the WAN connectivity part of the architecture. SD-WAN helps route traffic across available network links. SASE adds security services around that traffic so branch internet access does not become a new risk.
What Is the Difference Between SASE and SSE?
SASE combines networking and security, while SSE focuses on the cloud security services portion. SSE usually covers secure web gateway, CASB, ZTNA, DLP, and similar controls. If you also need branch routing and WAN modernization, SASE is the broader model.
Is SASE Better Than VPN or SD-WAN Alone?
Yes, SASE is usually better for distributed organizations than VPN or SD-WAN alone. VPN can be too broad, and SD-WAN can lack complete security controls by itself. Still, the right path depends on your existing network, risk profile, and migration budget.
How 1Byte Supports Secure Website and Cloud Infrastructure
1Byte supports secure website and cloud infrastructure through practical services that sit around the broader access and hosting picture. SASE protects how users and sites connect to apps and data. Our role is different but related: we help customers establish and run the web and cloud foundations those users may access. As an AWS Partner, we also understand why secure cloud infrastructure needs careful planning from the start.
| 1Byte service | How it relates to secure infrastructure | Typical need |
|---|---|---|
| Domain registration | Creates a controlled public identity for a site or app | Launch a business website or customer portal |
| SSL certificates | Encrypts browser connections to websites | Protect logins, forms, and customer sessions |
| WordPress hosting | Hosts WordPress sites in a managed hosting context | Run a company website or content hub |
| Shared hosting | Hosts smaller sites with simple management | Publish a basic business presence |
| Cloud hosting and cloud servers | Run applications, data, and services in cloud infrastructure | Support apps that users access from many places |
Domain Registration and SSL Certificates for a Strong Security Foundation
Domain registration and SSL certificates help establish the public trust layer for websites and applications. A domain gives users a recognizable destination. An SSL certificate encrypts browser traffic so login pages, forms, and sessions are not sent in clear text.
This does not replace SASE. It complements it. SASE governs how users access resources, while domains and SSL certificates help protect the public-facing website path. We consider both basic hygiene. Skip either one, and the rest of the security conversation gets shakier.
WordPress Hosting and Shared Hosting for Protected Sites and Simple Management
WordPress hosting and shared hosting give organizations straightforward ways to publish and manage websites. For many small teams, the priority is not a complex network architecture. It is getting a site online with sensible management and protected connections.
SASE may protect the employees who manage that site, especially when they work remotely. Hosting protects where the site runs. Those are different layers, but they meet in daily operations. A marketing manager updating WordPress from home still needs secure access and a dependable hosting base.
Cloud Hosting and Cloud Servers for Scalable Apps, Data, and Remote Access
Cloud hosting and cloud servers support applications and data that users may access from many locations. That makes them closely connected to SASE planning. If users reach an app from branches, homes, and mobile networks, access policy and cloud infrastructure must be thought through together.
At 1Byte, we see this pairing often. The cloud server hosts the workload. The access architecture controls who can reach it, under what conditions, and through which path. When those decisions are aligned early, teams avoid painful redesign later.


Conclusion
SASE is a cloud-based architecture that unifies networking and security for a world where users, apps, and data are widely distributed. It brings SD-WAN, ZTNA, secure web gateway, CASB, DLP, firewall-as-a-service, and related controls into a more consistent access model. The big idea is simple: verify users, inspect traffic, protect data, and route access intelligently wherever work happens.
We believe SASE is most useful when it solves a real operational problem, not when it is bought as a buzzword. Start with the pressure point you can name clearly. Is it VPN risk, branch complexity, SaaS visibility, MPLS cost, or cloud access control? Once that answer is clear, the architecture conversation becomes much more practical.
If your organization is also building the web and cloud infrastructure that people need to access securely, look at the foundation first. Do your domains, SSL certificates, hosting, cloud hosting, and cloud servers match the access model you want? That is a good next question to ask before the next migration, redesign, or security review.