
- Desktop Virtualization Lets Users Reach a Desktop Environment and Its Apps From Another Device
- What the Desktop Includes
- How Remote Access Extends the Desktop Beyond One PC
- How Organizations Deliver and Manage Desktop Access
- What Matters for Security, Maintenance, and Reliability
- When Physical Desktops Still Shape the Experience
- Conclusion
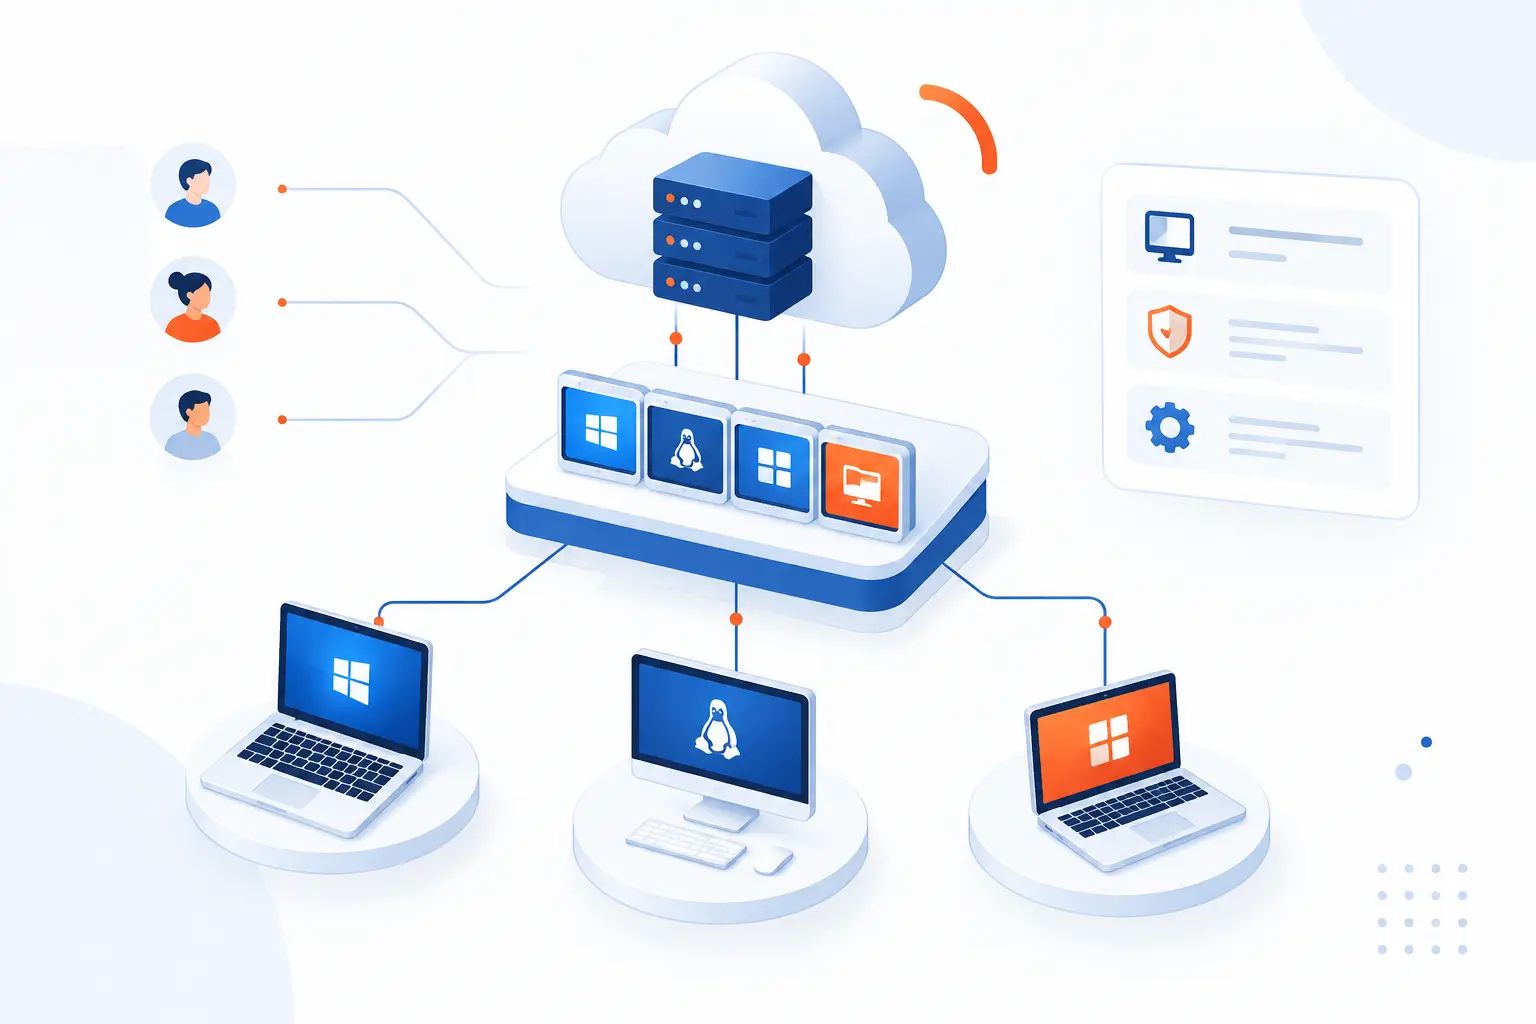
Desktop virtualization is a way to separate a user’s desktop environment from one specific physical computer, so the workspace can be reached from another device. The desktop may run in a data center, a cloud platform, or a centrally managed system, while the user sees files, apps, windows, and settings through a network connection. The big idea is simple: the work experience follows the user, not the box under the desk. We like this concept because it treats the desktop as a managed service instead of a fragile one-machine island.
For beginners, desktop virtualization can sound more mysterious than it is. It does not mean the keyboard, monitor, and mouse disappear. It means the operating system and applications may live somewhere else, while the user interacts with them through a client app or browser. That shift changes how companies handle access, security, maintenance, and hardware planning.
Desktop Virtualization Lets Users Reach a Desktop Environment and Its Apps From Another Device
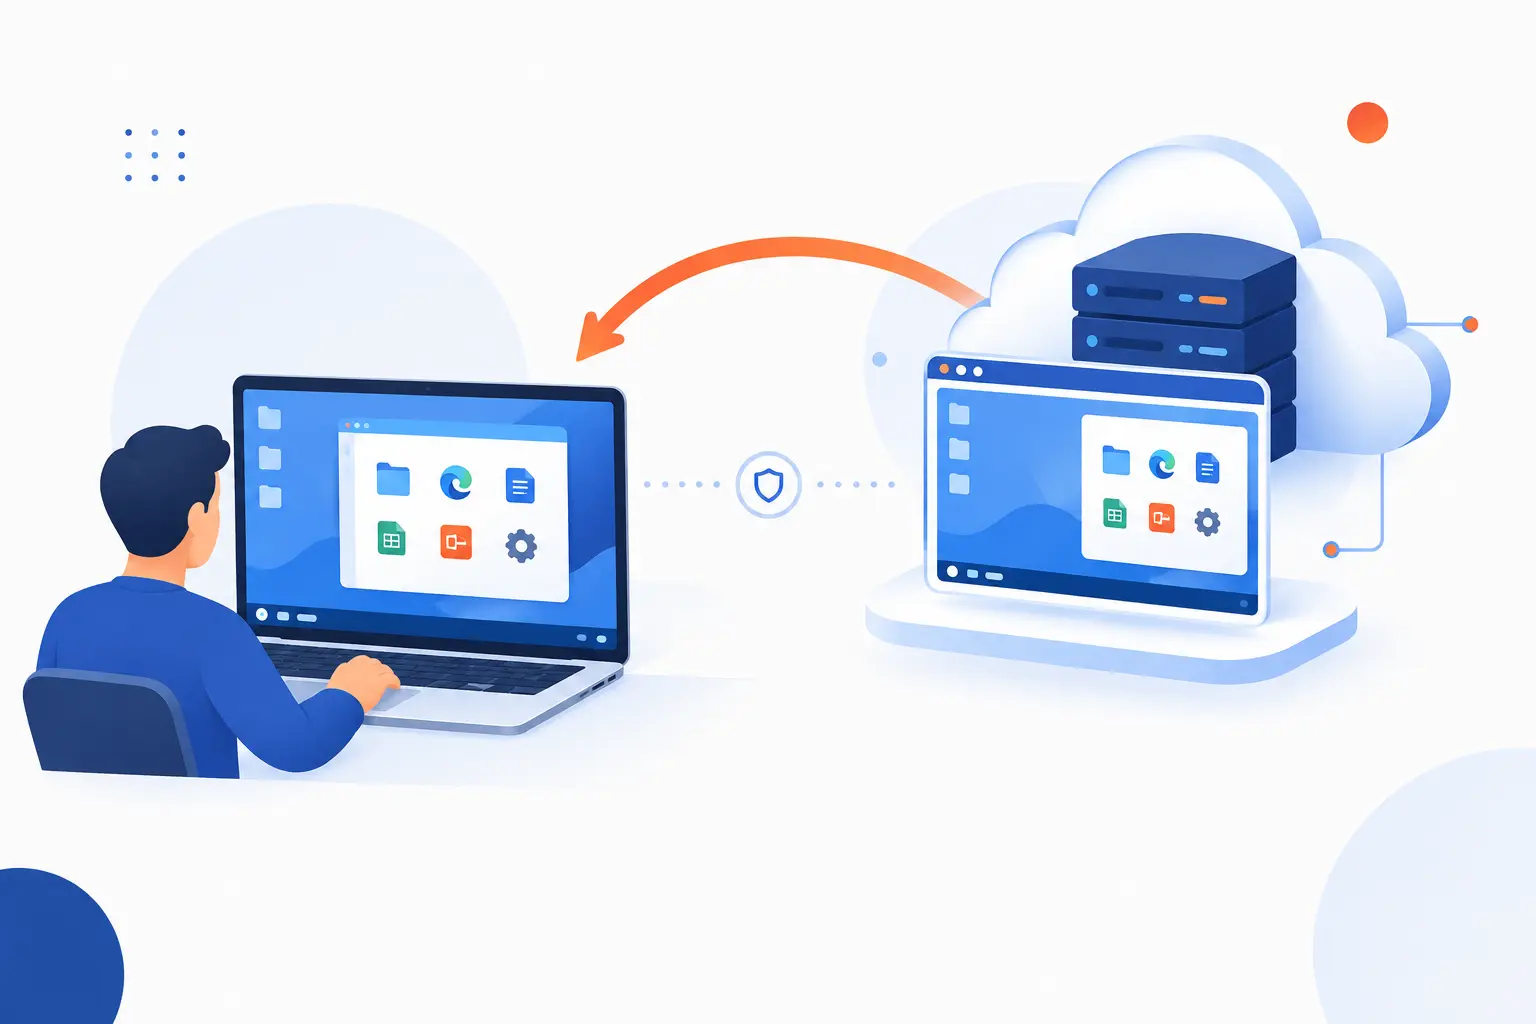
Desktop virtualization means delivering a full desktop environment to a user without tying that environment to one local PC. The user still sees a familiar workspace with apps, files, folders, and windows, but the computing may happen on a remote server, cloud-hosted machine, or managed endpoint. In practical terms, a finance employee can sign in from a laptop at home and reach the same work environment they used at the office. The device becomes the doorway, while the desktop becomes the place where work actually happens.
The clearest real-world examples are cloud-hosted workspaces and company-managed remote environments. A service such as Amazon WorkSpaces lets organizations provide hosted user environments through a managed offering described in its technical introduction. Microsoft takes a similar business-facing approach with Windows-based cloud workspaces that users can access through supported clients or a web browser. Different products package the model differently, but the user story is the same: sign in, open the workspace, and use the business apps.
We should be honest about the tradeoff. Desktop virtualization is not magic, and it does not remove the need for good networks, identity controls, endpoint security, or planning. What it does well is centralize the desktop experience so IT can manage it with fewer scattered moving parts. For companies with hybrid teams, contractors, regulated data, or standardized software, that central control can be the difference between order and a drawer full of unmanaged laptops.
FURTHER READING: |
| 1. Cloud Migration Strategy for Planning and Rollout |
| 2. What Is a Virtual Dedicated Server and How It Works |
| 3. How to Make a Minecraft Server for Java Edition |
What the Desktop Includes
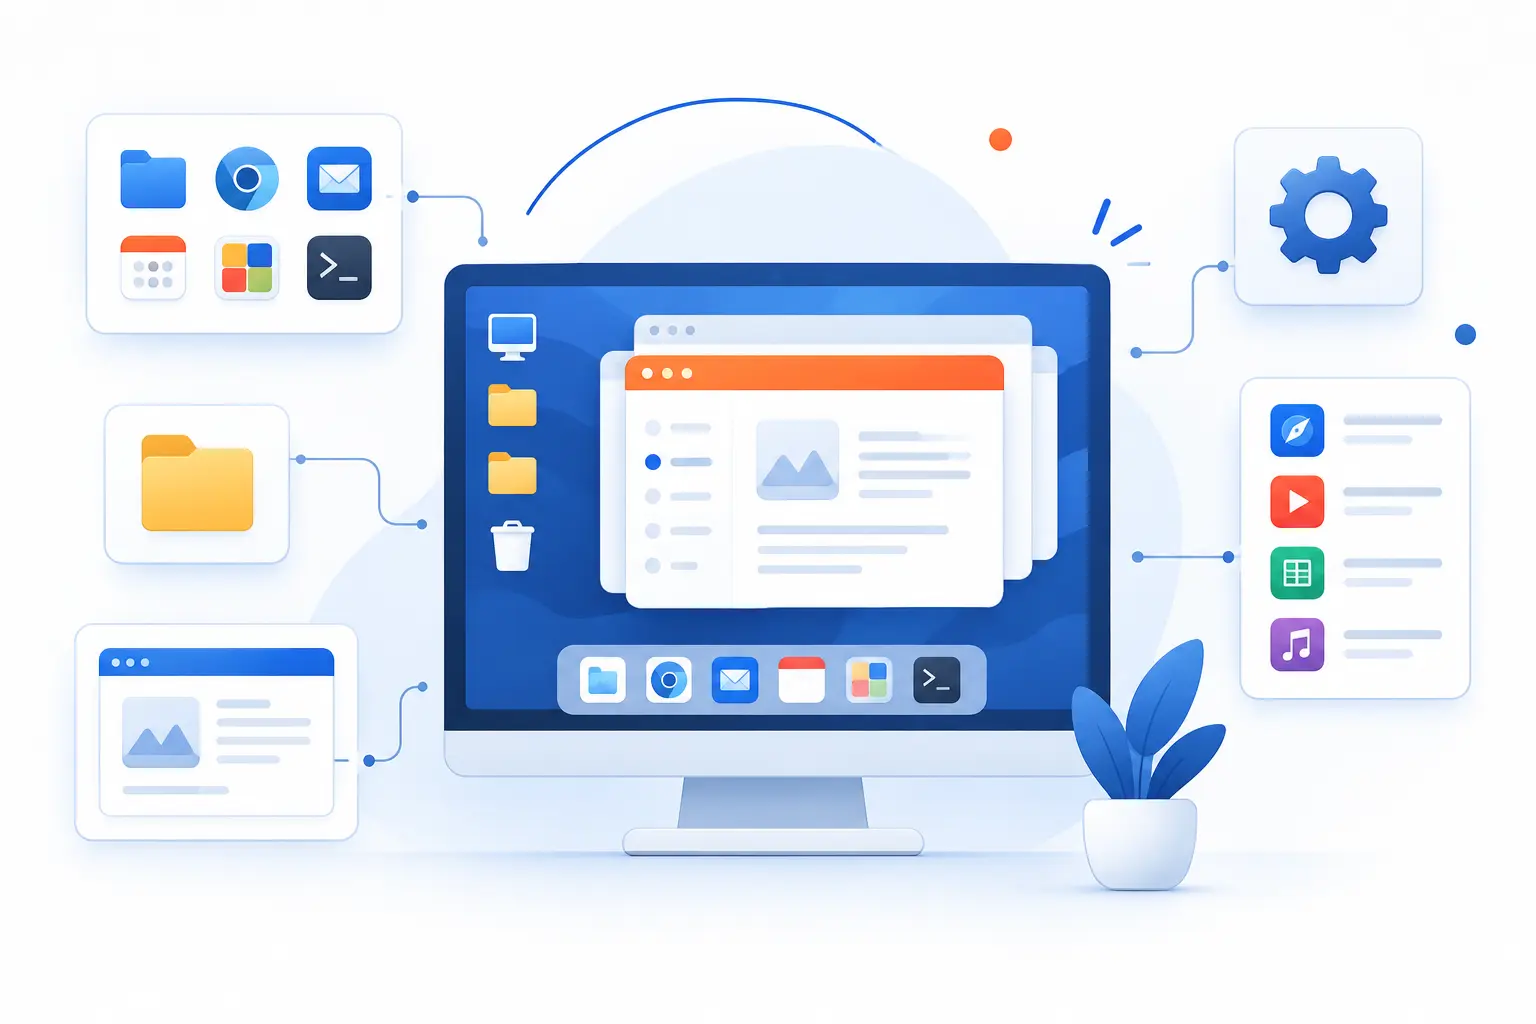
A desktop includes the visual workspace, the operating system, user settings, files, and the applications people use to do their jobs. In desktop virtualization, those parts may be streamed, hosted, synchronized, or remotely controlled, depending on the design. The user experience feels familiar because it keeps the same basic computer language: icons, folders, windows, menus, browsers, and apps. The underlying delivery model changes, but the mental model stays recognizable.
The Desktop Metaphor of Files, Folders, and Windows
The desktop metaphor gives users a visual way to organize work, even when the actual computing happens somewhere else. Files look like documents, folders look like containers, and windows act like separate work surfaces. That familiar design lowers the learning curve. A user does not need to understand hosting architecture to open a spreadsheet.
In a virtualized setup, the “desktop” shown on the screen is often a remote session or rendered workspace. The clicks, keystrokes, and screen updates travel between the user’s device and the system hosting the environment. To the user, it still feels like opening folders and dragging files. To IT, it is a managed session with policies, permissions, storage rules, and monitoring behind it.
This is why desktop virtualization works best when the interface gets out of the way. If latency is low and apps respond normally, most users stop thinking about where the desktop lives. If the connection is poor, they notice immediately. The metaphor is simple, but the experience depends on the network and platform beneath it.
The Operating System Behind the Workspace
The operating system is the engine that makes the virtualized workspace behave like a real computer. It manages user accounts, memory, storage access, devices, application processes, security controls, and the graphical interface. Whether the OS runs locally, on a server, or in a cloud-hosted machine, it still performs those core jobs.
In many business environments, the operating system is Windows because employees depend on Windows applications, Microsoft 365 tools, and familiar admin controls. Some environments use Linux for developer workstations or technical users. The right choice depends on software compatibility, licensing, user skill, and IT management needs.
The important point is that virtualization changes the location of the operating system, not its purpose. A user still signs in, opens programs, saves files, and applies settings. The difference is that IT may build, patch, restore, and protect that operating system from a central console instead of touching each machine one by one.
Business Applications Such as Browsers, Email, and Collaboration Tools
Business applications are the main reason users care about the desktop at all. A virtualized desktop is only useful if browsers, email, chat, document editors, accounting tools, line-of-business apps, and collaboration tools run well. The best architecture is the one that supports the actual work, not the one that looks neat on a diagram.
For basic office work, the workload is usually modest. A browser, email client, video meeting app, and file-sharing tool may be enough. For heavier work, the desktop might need more CPU, memory, storage performance, graphics acceleration, or peripheral support. We have seen teams underestimate this part. Then the “simple” workspace becomes slow because every user opens twenty browser tabs and joins video calls all day.
Application location also matters. Some apps run inside the remote workspace. Others run locally on the endpoint. Web apps may live entirely in the browser. A good plan maps each application to the place where it performs best and stays easiest to secure.
How Remote Access Extends the Desktop Beyond One PC
Remote access lets users interact with a desktop environment from a device that is not the original workplace PC. The user may connect through a dedicated client app, a browser, or a secure remote session. In desktop virtualization, remote access is the bridge between the endpoint in the user’s hands and the workspace where the work happens. Done well, it lets people keep working without copying sensitive files onto every device they touch.
Using Another Computer, Phone, or Tablet
Users can reach a virtualized desktop from many device types when the platform supports the right client. Microsoft’s access requirements, for example, list support paths across Windows, macOS, iOS/iPadOS, Android, Linux, and browser-based access through its client guidance. That matters because the endpoint is often just the entry point. The main work environment can stay consistent even when the user switches devices.
A laptop is still the most comfortable option for long work sessions. Phones and tablets are useful for approvals, quick checks, emergency access, and travel situations. We would not ask a designer to edit a complex layout from a phone, but we would expect a manager to review a document or restart a meeting from one.
The endpoint still needs enough local capability to display the session, handle input, and support audio or video when needed. A weak device can connect, but it may not deliver a good experience. That is especially true for video meetings and multiple monitors.
Viewing Files and Running Programs From Anywhere
Desktop virtualization lets users view files and run programs from outside the office while keeping the main workspace under company control. Instead of copying a customer database to a personal laptop, the user can open it inside a controlled environment. That distinction is not just technical. It changes the risk profile.
When files remain in the managed workspace, IT can apply permissions, logging, backup, encryption, and data loss controls more consistently. Users still get the practical benefit of access. The company gets fewer loose copies of sensitive information.
There is a catch, of course. “From anywhere” does not mean “from any unsafe network with no controls.” Organizations still need identity checks, device posture rules, session policies, and user training. A virtual desktop is a strong tool, but it is not a substitute for security discipline.
Connecting for Collaboration and Remote Support
Remote connections also help teams collaborate and let support staff troubleshoot without standing next to the user. A technician can inspect settings, review error messages, or guide the user through a fix. In some cases, the technician can work on the managed desktop while the user watches.
This is useful for distributed teams. A support person in one city can help an employee in another city without shipping a laptop back and forth. It also helps with training because a senior user can show a workflow inside the actual work environment.
Good support access needs boundaries. Users should know when someone is connected. Admin rights should be limited. Sessions should be logged where appropriate. We strongly prefer remote support models that reduce guesswork without turning every desktop into an open door.
How Organizations Deliver and Manage Desktop Access
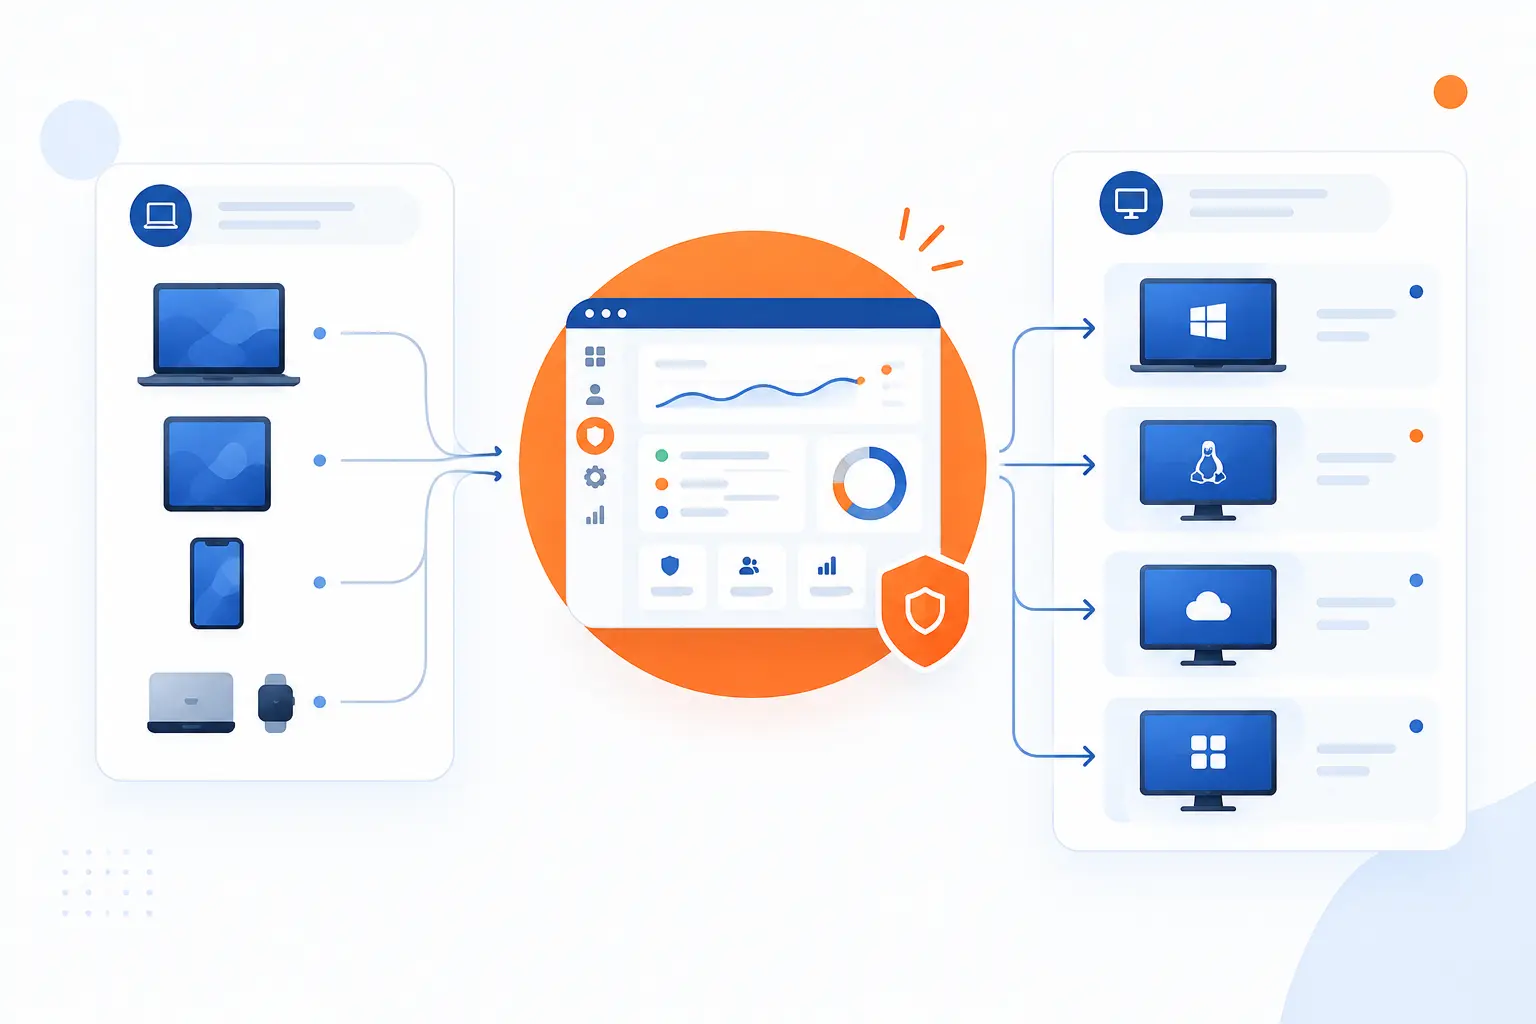
Organizations deliver desktop access by choosing where the workspace runs, how users connect, and how IT manages the endpoints. Some teams need standard office desktops. Others need developer workstations, engineering tools, or tightly managed business PCs. The right model depends on workload, security needs, application compatibility, and budget. We usually start by asking what the user must do all day, then work backward to the delivery method.
| Option | Best fit | Main tradeoff |
|---|---|---|
| General-purpose desktops | Office apps, browsers, email, routine business work | May struggle with heavy graphics or specialized tools |
| Developer or engineering setups | Code, builds, design tools, simulation, technical workloads | Needs stronger compute, storage, and network planning |
| Thin client configurations | Controlled environments and shared work areas | Depends heavily on the remote platform |
| Thick client configurations | Users who need strong local performance | More endpoint maintenance remains |
| Centrally managed PCs | Standard company laptops and desktops with admin control | Still tied partly to physical hardware |
General-Purpose Desktops, Developer Workstations, and Engineering Setups
Different users need different virtualized desktop profiles because their workloads are not equal. A customer support agent may need a browser, CRM, softphone, and email. A developer may need an IDE, package manager, local test services, and secure access to repositories. An engineer may need CAD, rendering, simulation, or GPU acceleration.
This is where one-size-fits-all planning falls apart. If every user gets the same low-cost desktop, the power users complain. If every user gets the biggest configuration, the budget burns. A better approach is to group users by workload and assign the right level of compute, memory, storage, graphics, and access.
We also look closely at data gravity. If applications and data already live in a cloud platform, placing the desktop near those systems can reduce back-and-forth traffic. If data sits in an on-premises file server, remote users may need a different path. Performance is often about distance, not just specs.
Thin Client and Thick Client Configurations
Thin clients rely on the remote environment to do most of the computing, while thick clients keep more power and software on the local device. A thin client may be a small dedicated terminal, a locked-down device, or an older PC repurposed for access. A thick client is a full-featured laptop or desktop that can run apps locally as well.
Thin clients are attractive when a company wants simple endpoints, fewer local files, and tighter control. They can work well in call centers, shared desks, labs, and task-based work areas. If a unit breaks, replacement is often easier because the user’s main environment is elsewhere.
Thick clients make sense when users need strong local performance, offline work, specialized peripherals, or heavy video use. They cost more to manage because the endpoint remains important. Still, they are often the right choice for executives, designers, field workers, and technical staff who cannot depend on a remote session every minute.
Centrally Managed Business PCs With Remote Administration
Centrally managed PCs keep the desktop on company hardware while giving IT remote control over policy, updates, and support. This is not always full desktop virtualization, but it often sits beside it in the same access strategy. A company may use virtual desktops for contractors and managed laptops for employees, with both controlled through identity and policy.
Modern endpoint management tools can push settings, collect diagnostics, restart devices, lock devices, sync policy, or wipe lost machines. Microsoft documents these kinds of administrative actions in its management reference. That type of control matters because physical laptops still leave the office, get misplaced, and connect from unpredictable networks.
From our point of view, the practical goal is not to force every user into one model. It is to create a manageable estate. Some desktops run in the cloud. Some live on local machines. Some are hybrids. The winning pattern is the one IT can secure, patch, recover, and explain.
What Matters for Security, Maintenance, and Reliability
Security, maintenance, and reliability matter because desktop virtualization concentrates access to important applications and data. A well-designed environment can reduce scattered risk, but a poorly designed one can centralize mistakes. The essentials are identity, encryption, patching, monitoring, endpoint protection, backup, and clear administrative ownership. We see desktop access as infrastructure, not just a convenience feature.
Secure Infrastructure and Modern Web Technologies
Secure infrastructure starts with verified identity, protected connections, segmented access, and monitored systems. NIST’s zero trust guidance describes a model where access decisions are made per request and depend on context, not blind network trust, in its security model. That thinking fits virtualized desktops well because users may connect from many places and devices.
Modern web technologies also matter. Browser-based access can reduce installation friction, especially for temporary access or unmanaged devices. Dedicated clients may offer stronger device integration, better peripheral support, or improved multimedia behavior. The best choice depends on the user group.
Encryption should protect traffic between the endpoint and the hosted environment. Admin portals should require strong authentication. Logs should show who connected, from where, and what administrative actions occurred. If that sounds basic, good. Basic controls done consistently beat fancy controls done halfway.
Application Security, VPN, and Antivirus Protection
Application security must cover the remote workspace, the endpoint, and the path between them. NIST’s telework and BYOD publication recommends securing all parts of remote work technology, including client devices and access systems, in its federal guide. That is the right mindset. A secure virtual desktop can still be undermined by a compromised endpoint or weak login process.
VPNs can still play a role, especially when users need access to private internal systems. However, VPNs need careful configuration, patching, and cryptographic controls. CISA and partner agencies warn that traditional network access can create business risk when misconfigured, and their joint notice points organizations toward more modern access planning.
Antivirus and endpoint detection tools remain useful, but they should not be the only shield. Application allowlisting, least privilege, browser protection, email filtering, and conditional access all reduce risk. We prefer layered controls because users make mistakes, software has bugs, and attackers do not stop at the first locked door.
Updates, Maintenance, and Enterprise Support
Updates and maintenance keep virtualized desktop environments stable, secure, and supportable. The main tasks include operating system patching, application updates, image management, profile cleanup, certificate renewal, backup testing, and capacity review. Skipping these jobs turns a clean desktop design into technical debt.
Centralization helps here. If IT maintains a base image or controlled workspace pool, updates can be tested once and rolled out consistently. That beats chasing dozens of one-off laptops with different app versions and mysterious settings. Still, change control matters. A bad image update can affect many users quickly.
Enterprise support should define who owns each layer. One team may manage identity. Another handles networks. Another owns endpoint policy. A cloud or hosting partner may operate infrastructure. Clear ownership avoids the classic support loop where every vendor says, “not our part.” We have sat in those calls, and nobody enjoys them.
When Physical Desktops Still Shape the Experience
Physical desktops still shape the user experience because screens, keyboards, cameras, local networks, GPUs, RAM, and peripherals affect how the remote workspace feels. Desktop virtualization moves the workspace away from one machine, but the user still touches real hardware. A bad monitor, weak Wi-Fi connection, or underpowered endpoint can make a well-built remote environment feel poor. The cloud can host the session, but the user lives at the edge.
Business Towers and All-in-One Systems
Business towers and all-in-one systems can still be practical endpoints for virtualized desktop access. They provide stable desks, wired networks, full-size displays, and predictable peripherals. In offices, classrooms, labs, and front-desk environments, that consistency is valuable.
A tower gives IT more room for upgrades and repairs. An all-in-one reduces cable clutter and keeps the desk simpler. Neither choice is glamorous, but both can make remote access feel better because the endpoint is comfortable and reliable.
These machines may also run local apps beside the virtualized workspace. That can be helpful, but it needs policy. If sensitive files move between local storage and the remote environment without control, the security benefit weakens. We prefer clear rules about what stays local and what belongs inside the managed workspace.
Workstations for Rendering, Simulation, and AI
Workstations remain important when users need high-end graphics, large memory, specialized drivers, or predictable compute performance. Rendering, simulation, AI development, video production, and CAD workloads can stretch ordinary virtual desktops. These users need careful design, whether the power sits under the desk or in a remote GPU-enabled environment.
Virtual GPU software can help bring graphics acceleration to hosted environments. NVIDIA describes a model where a physical GPU can be shared across multiple machines through its software guide. That can work well for certain professional workloads, but it must be matched to application requirements, licensing, display needs, and user expectations.
We do not recommend guessing here. Test the real application with real project files. Measure launch time, input delay, render time, display quality, and stability. A light demo can look fine while a production model crawls. Engineers and artists will notice the difference before the first coffee break.
Limits Around RAM, Graphics, and Connectivity
RAM, graphics, and connectivity set hard limits on the quality of a virtualized desktop experience. A remote workspace may have plenty of server-side resources, but the endpoint still needs enough capacity to decode display updates, support monitors, process audio, and handle local devices. Microsoft’s listed baseline for one Windows client includes 1vCPU with 1 GHz, 1024 MB RAM, and 100 MB, while richer scenarios require more.
Graphics are another common bottleneck. Multiple high-resolution monitors, video calls, 3D apps, and design tools need more than a bare-minimum endpoint. If the remote environment uses GPU acceleration but the local device has poor display support, users may still see lag or artifacts.
Connectivity is often the deciding factor. Latency, packet loss, jitter, Wi-Fi quality, and internet routing affect every click. Faster bandwidth helps, but stability matters just as much. We would rather have a steady connection than a headline speed that drops every few minutes.


Conclusion
Desktop virtualization gives organizations a flexible way to deliver familiar workspaces without anchoring every user to one physical PC. The user sees apps, files, folders, and windows. Behind the scenes, IT can centralize access, manage policies, secure data, and support different devices.
The best use cases are practical ones: remote staff, contractors, standardized office users, secure access to business apps, and teams that need consistent environments. More demanding workloads, such as rendering or simulation, can still fit the model, but they require better planning. Hardware does not vanish. It simply moves to the places where it makes the most sense.
Our view at 1Byte is straightforward: treat the desktop as part of your infrastructure plan, not as an afterthought. Start with the user’s work, map the applications, test the network, and define the security rules before rollout. If you are evaluating desktop virtualization, your next step is to list your user groups and ask one blunt question: what does each group need to do without friction?